DuckDuckGo Takes Great Leap Forward In The Battle For Online Privacy

DuckDuckGo has seen an exponential increase in traffic as it continues to stand up for privacy by implementing Global Privacy Control

The decisions and choices we make now on how we operate online will decide the outlook of the digital landscape for decades to come. Protocols and standards we implement and attribute value to at this juncture will dictate what is tolerated in the future. One such standard is privacy; specifically our privacy online. Privacy should be a right by default, but it’s long been taken for granted on the internet. Worse so, it’s been abused by those who once espoused that they would protect it. Big Tech, and many of their related services have increasingly breached the inherit trust of their users by using their data without their consent.

These breaches haven’t gone unnoticed. Globally, in the last few years, many governments have made steps toward protecting their citizens privacy by introducing various laws to tackle privacy breaches; GDPR, CCPA, LGPD to name a few. If you live in a territory that benefits from one of these, you’ve certainly noticed changes to your general browsing experience – Long forms to fill out on blogs, intrusive pop-ups before you can view websites – it can be daunting. Moreover, many websites make use of Dark Patterns to bypass these laws, and grab your data without your consent regardless. To combat this issue, Global Privacy Control (GPC) was formed – with DuckDuckGo as one of it’s founding members.

Global Privacy Control
Global Privacy Control

Global Privacy Control is a new web standard, and it’s members make up some of the biggest names in online privacy – DuckDuckGo, Brave Privacy Browser, Abine, Disconnect, and more.

Rather than clicking through tedious forms, or even being forced to opt-in without consent, the GPC approaches the problem with a global and by-default solution. In shorts, a user would use a platform which has GPC built in, enable the global switch, and the browser will then send the GPC signal via the browser to whichever website is being visited. It’s a hands-off method for the end user, where they get to exercise their rights to digital privacy without the need for legwork.

Beneath the hood, the implementation is simple enough. With GPC enabled when you visit a website, there will be a ‘Sec-GPC header‘ the website will be able to read. If the value is read as ‘Sec-GPC-field-value = “1”‘ , it means the user has revoked all permissions for their data to be sold to third parties. Giving users the ability to easily control their privacy like this is just the first step to ensuring that privacy can remain a given right, and not something taken from us so easily.

Implementation of GPC by DuckDuckGo

DuckDuckGo has long been an advocate for online privacy , since their foundation in 2008. Being a founding member of GPC, an implementation was expected. In late January 2021, DuckDuckGo announced that they would be implementing GPC in their apps and extensions.

With it enabled, DuckDuckGo users will automatically exercise their opt-out under legislation such as the CCPA and GDPR.

The implementation of GPC is a welcome addition to DuckDuckGo’s toolkit, which already boasts a number of privacy policies; including protecting it’s users from being profiled in their search results, and compatibility with TOR.
DuckDuckGo

The new changes come to DuckDuckGo at a time when privacy is once again in the spotlight – WhatsApp made headlines as it changed it’s privacy policy and caused users to flock en masse to alternative services such as Signal and Telegram. Facebook, who have owned WhatsApp for a number of years, already have their hands full with Apple – who recently made steps themselves to give their users more control over their privacy by default, which would affect personalized advertising. Apple’s decision caused Facebook to lash out, and they went as far as taking out full page ads in the New York Times, Wall Street Journal, and Washington Post criticizing the move.

DuckDuckGo as a rival to Google
DuckduckGo v Google

For better or worse, Google has been become the leading authority in the search engine game and how we browse – So much so that their name has become classified as a verb meaning to search the world wide web.

DuckDuckGo is one of many alternative search engines to Google, but due to their emphasis on privacy, they have pulled ahead of the competition. Online privacy, once only a concern of the most die-hard techies, makes headlines more frequently as the years roll on. This can be seen in DuckDuckGo’s traffic – in 2020, they received 23 billion search queries. 2019 saw 15 billion queries, and the previous year saw 9 billion – a growth rate which is nothing less than exponential.

It is not known exactly how many people use DuckDuckGo; due to their rigid privacy rules they don’t know themselves, but their future, and the future of user’s privacy globally, is looking bright.
Virtual Private Networks

VPN’s, or virtual private networks, have nearly become a household term in recent times. Once being used almost exclusively by businesses, VPNs found favor with journalists and freelancers who needed anonymity for one reason or another, and eventually became popular in countries where Internet censorship and restrictions began to take place. Fast forward to the 2010s, VPNs evolved and gave themselves purpose to appeal to nearly every type of Internet user; be they ordinary people looking to stream on geo-locked services, individuals with privacy concerns, or small businesses trying to set up a cybersecurity solution with minimum overhead. Today, escaping the VPN is nearly impossible – YouTubers, Podcast Hosts, and even TV talk-show hosts are all endorsing various VPN companies. It’s easy to view VPN’s are an add-on for security, but in actuality they’ve become a necessity; the bare minimum of cybersecurity is no longer sufficient to remain secure in an increasingly connected society.

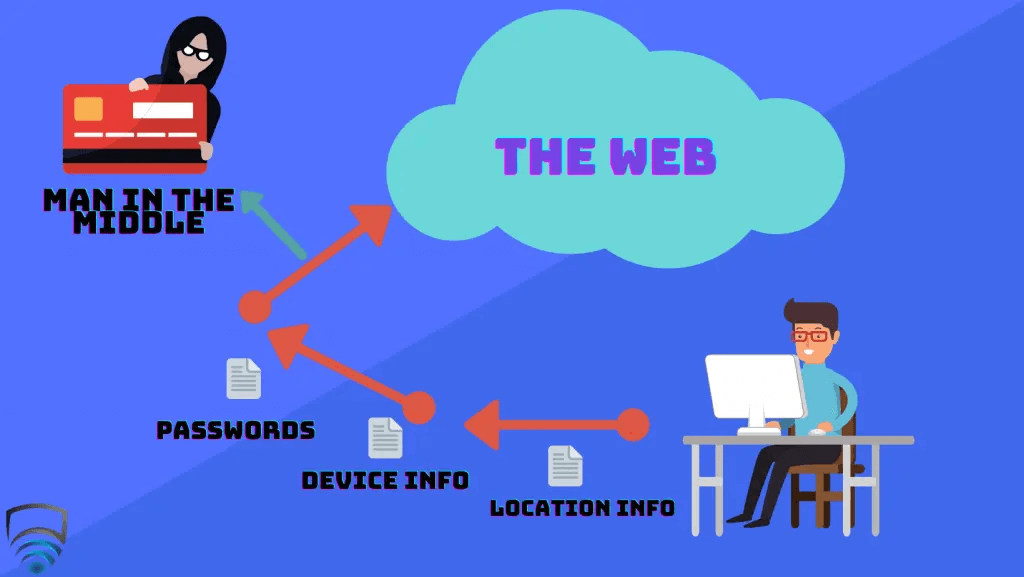
At a purely basic level, a VPN is used to encrypt your data and add a layer of privacy to protect your identity. Often, VPN’s are described as a ‘tunnel’ that your connection enters and accesses the web through. Usually when you connect to the internet, you do so via your internet service provider (ISP) and your connection is unprotected. In this state, the data you send to the internet is visible to anyone. This includes the the IP address of your device, your location, device information, and often times passwords and other private credentials. This is where the vulnerability lies; the most obvious man in the middle who wants to intercept your data here are hackers, but in the modern age you also have to deal with governments, advertisers, and even your own ISP. This is where a VPN comes in.

VPNs

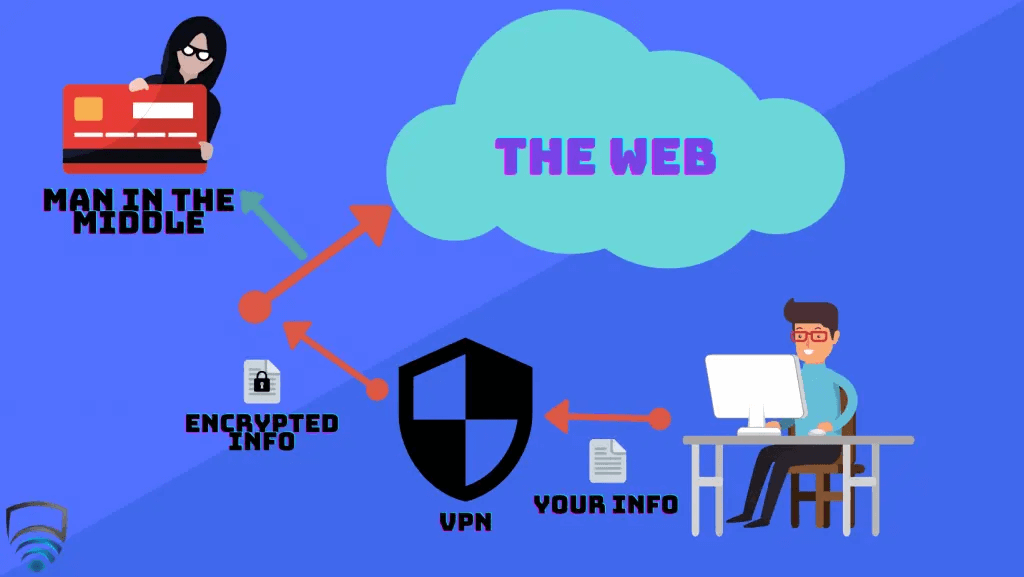
With an active VPN, the data no longer directly goes from your device and to the Internet. Instead, the data first goes through the VPN’s server, and then to the Internet. The connection between your device and the Internet is now in this ‘tunnel’ we mentioned earlier. The key here is that if an entity in the middle does try intercept your data, all they will see is encrypted traffic – Obfuscated information that makes little sense to the viewer, and in the majority of cases, cannot be deciphered. Any party that requests your data would instead be lead the VPN server, and your footprint remains anonymous. Many VPN companies opt to host their servers in a wide variety of locations and this is probably what VPN’s are most known for to everyday people – Location spoofing. Very simply, when you access a VPN server in a different location such as another country, when the VPN server directs your data to the Internet is appears as if you are active from that new location. This has a range of benefits, mostly commonly to view geo-locked streaming services, or booking hotels and flights who’s price vary depending on the buyers location.
VPNs

In non-technical terms, Encryption Protocols and Ciphers are what define the strength, complexity, and resilience of the ‘tunnel’ that protects your data when using a VPN. This is where some VPN companies differ; Though there are certainly industry-standards for both Protocols and Ciphers, different companies may choose different options for a variety of reasons. OpenVPN is a standard Protocol used by most VPN providers, which itself makes use of TLS and SSL Protocols. IKEv2/IPsec also provides comprehensive VPN coverage and is engineered for clients that swap connections often, which makes it ideal for mobile devices. L2TP/IPsec, a proprietary Microsoft Protocol, has it’s uses especially for legacy devices, but can easily be blocked by system administrators and has generally slow performance. SSTP, another Microsoft Protocol, offers the advantages of OpenVPN but is mostly only available on Windows devices. SSTP also suffers from being closed-source, which makes it difficult to scrutinize by researchers. The decision for what Cipher to take is much easier – Advanced Encryption Standard (AES) is the industry standard across the board, offering both AES-128 and AES-256; the latter being more favorable. ‘256’ refers to it’s key-length, and brute forcing through this would take billions of years to run through each possible combination. Overall, the average end user shouldn’t be overly concerned with what types of Protocol and Cipher are being used – Any of the above mentioned will trump an unprotected connection at any time.

VPNs

As VPN’s evolve into a more consumer friendly product, they have become a key weapon in any cybersecurity toolkit. Ten years ago VPN’s were marketed to the public with primarily location spoofing in mind, but VPN’s offer much more now, including malicious website blocking via DNS filtering, as well as parental controls. Businesses have made use of modern VPN’s not just for their inherit cybersecurity, but for their network monitoring capabilities to keep an eye on employees. The same is said for families running parental controls, where parents can now have a view into what their children are viewing online. Cybersecurity is an ever-changing industry, and there are alternatives to VPN’s rising and falling frequently – What’s clear is that given their low-cost, easy setup, and pure accessibility, VPN’s have their role in our online society, and are here to stay.

State Sponsored Hackers Attack US-Based Cybersecurity Researchers

In January, it came to light that state sponsored hackers attacked US-Based cybersecurity researchers. As of February 1st, Google researchers believe the attack is still on-going; a part of a larger campaign by the government of North Korea that has been happening for many months.

The attack was carried out via social engineering, followed by an attempt to install malware on the target’s machine, which would act as a backdoor. With this backdoor in place, the culprits would be able to gather intel on the researchers work; possibly around vulnerability the research community as a whole were working on.

Attack Methodology

Hacker Attack

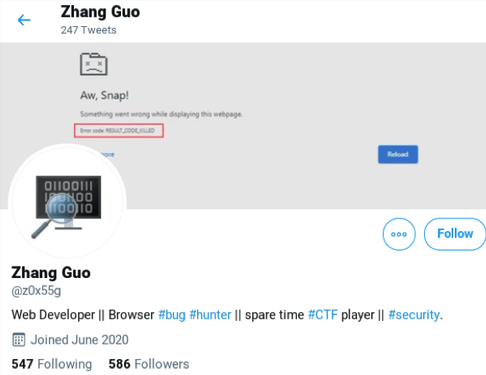
Twitter Account belonging to one of the attacks

In order to gain trust within the research community, the hackers created Twitter accounts – These were linked to their own “research” blogs. From these accounts they would share what you’d expect from a researcher – tweets on their own research including videos, retweets from other researchers, and links to their own blogs and others.

These actions helped build credibility and a sense of legitimacy in their Twitter accounts.

As their blogs increased in popularity, they often has guest bloggers – Legitimate individuals from within the research community. This, again, helped the hackers credibility.

Once they had established themselves on Twitter, the next phase began. The hackers started to reach out to researchers on Twitter via private message.

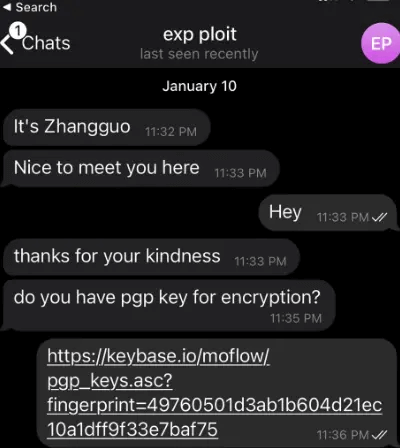
The state sponsored hackers proposed to the target that they should collaborate on research together. Once the target seemed interested, the conversation would then continue via Telegram.

Hacker Attack

Conversation on Telegram between one of the hackers and researcher Richard Johnson

The collaboration was around vulnerability research, and the hacker would provide the target with a Visual Studio Project. Within the Project was the exploit source code, and a DLL. Upon installation, the DLL would immediately begin to communicate with domains controlled by the hackers. Together, these would provide a backdoor into the researchers machine.

It is currently unknown how many targets the attacks were successful on. One such target, cybersecurity researcher Richard Johnson, had run the Project on a Virtual Machine (VM), and was unscathed.

Additional Attack Vectors

Since details of the initial attacks became public, Google’s Threat Analysis Group (TAG) have identified a separate attack vector linked with the same state sponsored hackers.

The blogs created by the hackers were shared on numerous socials – Reddit, LinkedIn, Discord, and the aforementioned Twitter.

Specifically, one blog titled ‘DOS2RCE: A New Technique to Exploit V8 NULL Pointer Dereference Bug’ was shared from October 14th 2020 onward. It was discovered by Microsoft that the simple act of clicking the link to this blog would deploy malware to the victims browser. The malware would reach back to the hackers controlled domains and execute malicious javascript. It is thought that the attack was successful on a up-to-date versions of Chrome, leading Google to remark that it took advantage of a zero-day vulnerability.

Identity of the state sponsored hackers

Hacker Attack

It is suspected the attackers behind these events are a part of ZINC, which works under Lazarus Group. Lazarus Group first came into the public spotlight when they carried out Operation Troy, which ran between 2009 and 2012.

Operation Troy was a series of distributed denial-of-service (DDos) attacks targeting government establishments in Seoul, South Korea.

Lazarus Group made the news again, identifying themselves as ‘Guardians of Peace’, in November 2014 for carrying out the Sony Pictures hack. During the attack, confidential data of many Sony Pictures employees were released, and initially circulated on Reddit. This attack is notable in the history of Lazarus Group; it was carried out in a sophisticated and complex manner, showing the group were now developing their skills rapidly.

Lazarus Group have also been responsible for a number of digital bank-heists; and the amount seized is believed to be at least $97 million.

The WannaCry ransomware attack of 2017, which saw a number of healthcare systems including the NHS in the UK brought to a halt, is believed but not confirmed to have been carried out by Lazarus Group.

As of today, Lazarus Group are involved in a number of additional attacks, notable the late-2020 pharmaceutical company attacks. By using spear-phishing methods, members of Lazarus Group acted as health officials and reached out to a number of pharmaceutical companies. Once trust was gained, Lazarus Group sent a number of malicious links to the companies. It is unconfirmed what the goal of the attack was, but it is suspected that they were looking to sell data for profit, extort the companies and their employees, and give foreign entities access to proprietary COVID-19 Research.

State sponsored hackers in the past

Hacker Attack

State sponsored hackers have been one of the largest forces behind cyberattacks for decades. Other notable state sponsored hackers include Bureau 121, Cozy Bear, The Shadow Brokers, Iranian Cyber Army, Red Apollo, and Equation Group – to name a few.

While state sponsored hackers have been known to the authorities and others in the industry for many years, they became a headline when The Shadow Brokers stole a number of tools from the National Security Agency in 2016. Many of the tools have since been sold to other groups, and now form a cornerstone of many attacks we hear of today.

A notable attack carried out by state sponsored hackers carried out recently was the Solar Winds attack. The attack had been on-going for many months before detection, with many outlets naming it as the ‘Deadliest cyberattack in US History’ due to its scale.

Looking Forward

Attacks carried out by state sponsored hackers often leave long-lasting ripples, and this one by Lazarus Group is no exception. The sense of distrust in the cybersecurity research community has began to grow, though an attack like this can eventually bring a community closer together. In terms of silver-linings, best security practices have been brought to the front such as running Projects and other files within a VM.

Both Google & Microsoft are continuing their research into this incident, as are the cybersecurity researchers on Twitter – the good ones. How far this has reached remains yet to be seen.

The Rise of Cyberattacks During the Pandemic

With the advent of the Coronavirus, or COVID-19, there has been a large spike in global internet activity; be this from individuals having to self-isolate, kids out of school, or the masses of employees who are currently working from home. Sadly, this has lead to a monumental increase of cyberattacks from bad actors; hackers both professional and amateur, taking advantage of an event when we as people are reliant on the web more than ever. These have mostly taken the form of Phishing attacks. Phishing is the fraudulent attempt to obtain sensitive information such as usernames, passwords and credit card details by disguising oneself as a trustworthy entity in an electronic communication. Phishing Scams are happening across all Social Media, Text and Email platforms. It’s hard to know what websites and shared links are safe and legitimate.

Here at SaferNet, we strive to make the Internet a more secure, safer environment. We offer a reliable and robust VPN (Virtual Private Network) that can be used on any device to supply complete protection against phishing scams, malicious attacks, assaults on your network, hacks, and much more. Now, its is more important than ever to protect yourself from digital scams, viruses, and malware. Below, we have outlined some of the most common types of Phishing attempts – What to know, what to look out for, and how to protect yourself.

Email Phishing

Cyberattacks

Most phishing attacks are sent by email. The crook will register a fake domain that mimics a genuine organization and sends thousands out thousands of generic requests. The fake domain often involves character substitution, like using ‘r’ and ‘n’ next to each other to create ‘rn’ instead of ‘m’. Alternatively, they might use the organization’s name in the local part of the email address (such as [email protected]) in the hopes that the sender’s name will simply appear as ‘PayPal’ in the recipient’s inbox.

At a time where many governments are planning on sending their citizens financial relief for those out of work during the Corona Pandemic, there has been an enormous spike in Email Phishing. Hackers pose as government officials, social security workers, and more to try get innocent people to part with their details. These attacks are extremely effective against those who are not tech savvy. There are many ways to spot a phishing email, including double-checking email addresses, but as the attacks become more sophisticated, these are getting harder to spot. One sure way to protect you, your employees, or your loved ones against getting duped is to use SaferNet. SaferNet will block all email phishing attempts. If the target opens the email, and accesses the link, SaferNet will target the link automatically and block it, ensuring your data remains in your hands.

Angler Phishing

Cyberattacks

A relatively new attack vector, social media offers a number of ways for criminals to trick people. Fake URLs; cloned websites, posts, and tweets; and instant messaging (which is essentially the same as smishing) can all be used to persuade people to divulge sensitive information or download malware. Alternatively, criminals can use the data that people willingly post on social media to create highly targeted attacks. In 2016, thousands of Facebook users received messages telling them they’d been mentioned in a post. The message had been initiated by criminals and unleashed a two-stage attack. The first stage downloaded a Trojan containing a malicious Chrome browser extension on to the user’s computer. When the user next logged in to Facebook using the compromised browser, the criminal was able to hijack the user’s account. They were able to change privacy settings, steal data and spread the infection through the victim’s Facebook friends.

These kind of attacks have been on the increase with regards to targeting kids especially, where malicious links are embedded in most commonly YouTube videos, but have also been seen on Instagram. Angler Phishing is soaring, with nearly every person in the globe being involved with some type of social media. As this type of Phishing becomes more sophisticated and harder to detect, SaferNet is ahead of the pack in being the only reliable method to avoid you or your loved ones having their details or accounts compromised.

Smishing (SMS Phishing)

Cyberattacks

With Smishing, telephones replace emails as the method of communication. Smishing involves criminals sending text messages (the content of which is much the same as with Email Phishing). A common smishing scam involves a criminal posing as a fraud investigator (either from the card company or the bank) telling the victim that their account has been breached. The criminal will then ask the victim to provide payment card details to verify their identity or to transfer money into a ‘secure’ account – by which they mean the criminal’s account.

Sometimes they will take the form of a fake direct-message or a cancellation link, which are often designed as a fake page you trust that gathers personal data. These are extremely common, and during the pandemic have seen an increase in popularity; Similar to Email Phishing, the criminal may pose as a government official looking for personal details to issue financial relief. The transaction of course never takes place, and the target is duped. SaferNet provides a shield against Smishing, automatically blocking and quarantining any suspicious link found in these schemes.

Smishing (SMS Phishing)

Cyberattacks

There are two other, more sophisticated, types of phishing involving email. The first, spear phishing, describes malicious emails sent to a specific person. Criminals who do this will already have some or all of the following information about the victim:

  • Their name
  • Place of employment
  • Job Title
  • Email Address
  • Specific Information about their job role

One of the most famous data breaches in recent history, the hacking of the Democratic National Committee, was done with the help of spear phishing. The first attack sent emails containing malicious attachments to more than 1,000 email addresses. Its success led to another campaign that tricked members of the committee into sharing their passwords. These attacks are particularly aggressive in that they most likely already have your social media profiles and select target information. Using SaferNet 256-bit, bank-level encrypted VPN, you, your business, employees or family are safe against all attempts of spear phishing

Smishing (SMS Phishing)

Cyberattacks

Whaling attacks are even more targeted, taking aim at senior executives. Although the end goal of whaling is the same as any other kind of phishing attack, the technique tends to be a lot subtler and sophisticated like Spear Phishing

Criminals attempt to imitate senior staff, and scams involving bogus tax returns are an increasingly common variety of whaling. Tax forms are highly valued by criminals as they contain a host of useful information: names, addresses, Social Security numbers and bank account information. C-Suite posts that have higher access to large databases that can lead to organizational phishing attempts as employees and vendors trust the spoofed domain and potential important information. Banks, Technology, Healthcare are most targeted sectors for these attacks.

Conclusion

SaferNet, our 24/7, always-on, bank-grade VPN is your best, most reliable protection against not only phishing, but all forms of malware attacks during this time. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easy accessible control hub for you to monitor your network. While our monthly subscribers are guarded against all forms of attack, free users are left open to attempts like those listed above. Protect you, your employees, your loved ones, or your business today. Have peace of mind that your online and network Safety is assured.

The Infection Nobody Is Talking About

With a large portion of us now working from home, we are getting used to a new way of traversing our work day…

With this comes some changes, and some of us get more relaxed in our habits. You might dress more casually than you would in the office. You can play music or listen to podcasts on full volume. Your cat or dog can hang out with you all day. If you previously had a long commute to work, you can stay in bed a little longer in the morning.

The Infection Nobody Is Talking About

Without being in a physical office a lot of things can change, some for the better. You might experience issues too though – Your internet may not be comparable to the speed you get in the office, communication with colleagues takes a few more steps than it usually does, and probably worst of all, there’s no free coffee. There is however, one BIG thing you’re missing that you likely may not be aware of – You don’t have access to corporate cybersecurity.

Like having a spare set of car keys, having cybersecurity is not something people realize they’re missing until they really, really need it – and that point, it’s too late. Most businesses will have some form cybersecurity in their systems, or a whole in-house IT team to look after it.

door keys

Most businesses are also entirely unprepared for this historic moment in time; when they have to send the majority of workers home completely unprotected from cyber threats.

Many companies have seen their productivity decrease during this time but for hackers, data harvesters, cybercriminals and digital intruders it’s open-season. Unsecured networks, home security that is out of date, and working on personal devices; all of these circumstances create the perfect opportunity for the shadowy digital underground to strike. And that’s where we step in! SaferNet has empowered thousands of people to carry their own shielded protection against the masses of cybercriminals and crooks out there on the web. We’ve given kids, adults, senior citizens, and people from all walks of life a simple-to-use, easy-to-setup, all-in-one tool to live their digital life without worry, and in complete security.

SaferNet is an economical and smart solution to protect yourself from the dangers of the Internet. Best of all, you can try Safernet for 14-days, absolutely free. We can’t tell you how long these days will last; where social distancing and staying inside are the standard of the day, but we can guarantee that during these times and beyond, we will stand by your side as Guardians of the Internet. Spend time online without worrying, and without the fear of being a victim of cybercrime; Join SaferNet Today!

Online Protection For Families

For many families, the Coronavirus has changed day-to-day life at home. Parents are working from home, and kids are learning at home. If a child previously had little or no access to technology, they may suddenly have more – Some schools are operating online, and more games, chat, facetime and email come into the picture. Technology can be great tool, but with a stark increase in online times lately, its ugly side has become more visible – This great tool can be misused, and children can become a target for not only cyberattacks, but also inappropriate content. We’ve put together a few simple steps to help keep your kids safe online during this time, and how SaferNet can be your ally for it

CyberSecurity

Cyberattacks have always been a threat, but with an increase of people going online for longer sessions, the amount of cyberattacks have risen – by 37%. Like a thief trying to break into a house, the hacker will always look for the easiest route in, and in this case it’s the much younger ones in the family. A child may not be able to discern what sites, links, and emails are trustworthy, and a simple wrong click can mean giving an attacker access to the whole network. No matter what you or your child’s level of cybersecurity education is, SaferNet provides a frontline defense against dangerous clicks such as these – With our 256-bit VPN activated, any attempted journeys to the dark parts of the net will be immediately blocked, and your child’s device and network will remain untouched

CyberSecurity

Off-Time Schedules and Internet Off-Switch

Phones, tablets, laptops and desktops can serve as great entertainment at times like this, but it’s important to switch off from time-to-time too. This is perhaps more important during the pandemic due to the increased risk of internet addiction. Off-time scheduling is a great tool within SaferNet’s Internet Controls – using this, you can schedule users off-time. For example, a child may not need internet access during the night until the morning – With SaferNet, you make it so their devices have no internet connection from 8pm-7am. Similarly, the InterNet Off-Switch can be used instantly at times when you don’t want a child on their devices – dinner times, family times, etc.

CyberSecurity

Pornography

As mentioned previously, chat applications, emails, and other communication apps are becoming increasingly popular as kids look to stay in touch with their friends. Unknown to parents, there can often be inappropriate links sent around in these apps or emails, leading to porn, gore, violence, or other unwanted websites. No matter where the link comes from your kids device, we’re here to help. Any access to inappropriate content is stopped right away; we categorize the web into 84 categories, and you decide what’s inappropriate and what’s not.

CyberSecurity

Decide On What Apps Your Kids Can Use

It’s important to decide what apps your kids will be using during this time – For communication, gaming, and more. It’s not difficult for a child to download just about any app out there and use it in secret, but we can help with that. We have already identified nearly 50 apps that could be harmful, and can be blocked right now from SaferNet. Looking to block an app but it’s not on our list? Reach out to us, and we’ll add it our Allowed/Blocked Apps list right away.

CyberSecurity

Talk To Your Kids

Clear communication with kids about digital threats is invaluable. Talk to them – Are they aware of harmful risks in cybersecurity? Do they know there’s content out there that it’s not okay for them to see? Do they know about privacy and keeping private information to themselves – What are they posting online, and to who? Communication has always been key, now more than ever.

CyberSecurity

The global pandemic brings a lot of questions and worries, especially in the home. With SaferNet, the Internet doesn’t need to be one of them. Using SaferNet, you can ensure the protection of your little ones online, and ensure technology as a tool is being used the right way.

If you miss this, you’re missing everything

Have we slowed down enough to realize what’s really going on around us?

Most of the time we live for the next moment.

The next scroll.

The next swipe.

The next notification.

Right now we even anticipate the next bit of news declaring “projected peak of virus” or “what happened when this person decided not to stay home.” So much of our lives are centered around our next move, the next meeting, or the next experience. Have we really taken the time to realize how exhausting this becomes? Our company was created for one reason. To give you a choice where there used to be none.

pandemic

If you have SaferNet then you have a head start over anyone else. You are empowered to keep safe, stay private, and control your digital world. But there is ONE thing SaferNet cannot do. We cannot tell you what to do.

That, dear friend, is your choice and yours alone.

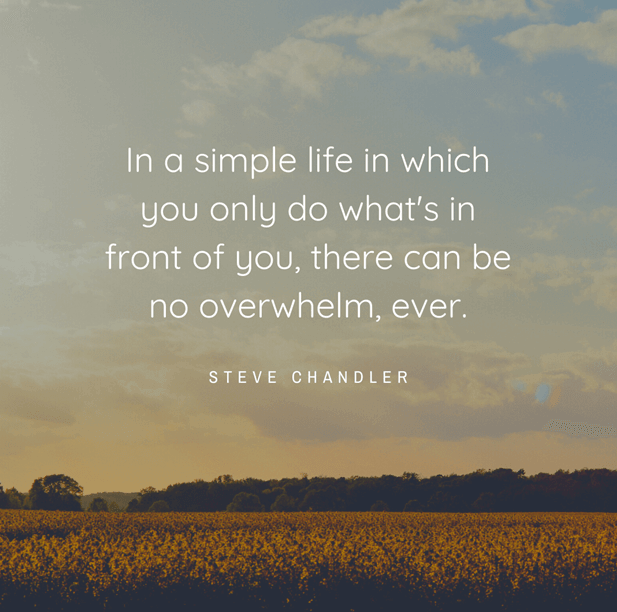
What is the choice before you right now? It is wrapped in that word “NOW”. It’s the choice to stay present. It’s the choice to engage with those right in front of you. Or to perform the task in front of you. What happens when we make this choice is remarkable. We increase the value either for the person or the task at hand.

pandemic

While this message is not focused on the capabilities of SaferNet, we wanted to address what you are going through. So many of us are staying home and living at a totally different pace than usual. We at SaferNet want to encourage you to make the choice to put the technology down and recognize what is going on around you.

pandemic

Raise the value of the moment.

Be well. Be present.

Hacking 101

Computers don’t create computer threats – People do. These people, hackers, victimize computer users for their own gain or for other motivations. Letting a hacker have access to the internet, and to your PC, the threat they post to your safety increases exponentially. Hackers, for the most part, are nefarious users who access computer systems without permission to manipulate or harvest data information or install viruses and other types of malware without your consent. Hacks are good at they do; they employ clever tactics and have a broad knowledge of IT systems which helps them to access private information that you really don’t want them to have.

There is sometimes a thought that one is only vulnerable to hackers if they use shady websites or services, but that’s not the case. Anybody using a phone, computer or just about any device connected to the internet can be exposed to the threats that hackers pose. These internet villains can use a whole host of techniques to deliver dangerous malware or compromise your computer security – spam email, phishing scams, bogus websites, trojans, and more.

Devices without protection are most vulnerable to these kinds of attacks. Conversations and transaction details can be monitored, social media accounts can be hijacked, and hackers can use false identities to lure you into giving over sensitive personal information, sometimes even financial.

What exactly can a hacker do to my device?

There are several ways a hacker can get information from your device – maybe malware has been installed without your knowledge which transmits your personal and financial informational, or maybe a phishing scam was successful, and you unwittingly gave the hacker information. There are plenty more methods, but whichever has been achieved, a hacker is able to:

  • Use your usernames and passwords
  • Use business accounts your device is connected to
  • Harvest any and all data
  • Spy on you
  • Advertise you in an invasive manner
  • Commit financial fraud
  • Impact your credit rating by misusing your bank information
  • Change PINs or add additional credit cards
  • Make online purchases
  • Commit fraud and other abuses with your social security number
  • Bundle your information into a package which can be sold on the dark web to the highest bidder

In severe cases, hardware can become damaged on a device, or entire operating systems may become fractured or unusable

How do I know if there’s been a breach or I’ve been compromised?

hacker

Very often, you will not know you’ve been hacked for quite some time. A recent study showed that US companies took an average of 206 days to detect a data breach.Cyberattacks are an increasingly serious risk for organizations, but many senior staff seem to believe that their organization won’t be targeted. They might say that their organization is too small to be on attackers’ radars, or that they don’t have anything worth attacking, but the truth is that cyber criminals are indiscriminate in their attacks and can almost always find something worth stealing.It is suggested all organizations should aim to identify a breach within 100 days. The average cost of identifying a breach within this time was $5.99 million, but for breaches that took longer to identify, the average cost rose to $8.70 million. There is a similar correlation in terms of containing a breach. Breaches that took less than 30 days to contain had an average cost of $5.87 million, but this rose to $8.83 million for breaches that took longer to contain. For a residential hack, on the family or individual, it may be more obvious, but sometimes there can be no indications at all. Here are some signs to look out for:

  • Fake AntiVirus Messages
  • Unwanted Browser Toolbars
  • Redirected Internet Services
  • Frequent random pop-ups
  • Your contacts receive emails from your accounts you never sent
  • Online passwords suddenly changed
  • Questionable or unauthorized bank charges
  • Changes to your social media pages you didn’t make

Some signs are more noticeable than others, and you should always be on the lookout for sudden or drastic performance and speed drops.

What can I about hackers?

Education is the first line of defense against hackers, along with resources created to protect and combat hackers

  • Have a protection, cybersecurity solution in place, like SaferNet
  • Use a VPN
  • Use 2-Factor Authentication, like Google or Apple
  • Update your operating system regularly
  • Keep an eye on personal records stored digital; financial or otherwise
  • Limit the personal information you post on social media
  • Keep personal and financial information out of online conversations
  • Keep your browser updated
  • Avoid questionable or shady sites
  • Only download software from sites you trust. Carefully evaluate free software and file-sharing applications before downloading them.
  • Don’t open suspicious messages, especially from senders you don’t know
  • Immediately delete messages you suspect to be spam
  • If opening suspect messages, have SaferNet active

The bottom line about online protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are fully protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories. Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service.SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all size of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.Protect your business or family with SaferNet today and have peace of mind that your online and network safety is assured.

Global CyberSecurity Report

Global CyberSecurity Report

A new survey from Arkose Labs revealed that the highest cyberattack rate was reported in the first quarter of 2020. The report suggested that 26.5% of all transactions during this period were fraud and abuse attempts, which is a 20% increase over the previous quarter. The survey “The Arkose Labs Q2 2020 Fraud and Abuse Report” also revealed that the U.S. has emerged as the top originator of cyberattacks, with attack levels increasing 20% since the previous quarter. It also found a significant increase in attacks originating from other well-established markets like the U.K., Germany, and Canada.

Global CyberSecurity Report cyberattack

The cybersecurity of many businesses worldwide has been in question since the beginning of the COVID-19 pandemic, as threat actors have used it to leverage various malicious attacks. However, the concerns seem to have elevated, as national and international bodies like the World Health Organization (WHO), Gates Foundation, National Institute of Health (NIH), among others, now face the wrath. Nearly 25,000 of their employees’ email addresses and passwords have been leaked and posted on the underground forums.

The data leak was first noticed by the SITE Intelligence Group, which monitors and analyzes the dark web for cybersecurity threats from online extremists and terrorist groups. The report from SITE stated that NIH was the worst affected with 9,938 leaked email addresses and passwords, followed by the Centers for Disease Control and Prevention at 6,857. Similarly, the World Bank had 5,120, and WHO had 2,732 employee email credentials being leaked. SITE also found that the data dump carries email addresses and passwords of a virology center in Wuhan, which has been at the center of many conspiracy theories related to the ongoing pandemic. Robert Potter, an independent Australian cybersecurity expert, the authenticity of the leaked data in a tweet, as he could verify some of the email addresses and passwords of WHO employees. However, he mentioned a possibility that this data could be from an earlier attack as health care organizations tend to take cybersecurity lightly at times. According to the Official Cybercrime Report published by Cybersecurity Ventures, the global pandemic of COVID-19 will continue to have a massive impact on cyberspace. The damages caused by cybercrimes are poised to double amid the Coronavirus outbreak. Cybercrimes will cost the world $6 trillion annually by 2021, up from $3 trillion in 2015.

Global CyberSecurity Report

Researchers from security firm Kaspersky have revealed a dangerous malware campaign called PhantomLance which has been apparently lurking in Google’s official Play Store marketplace. Dozens of malicious apps infected with the malware are being distributed via the Play Store and alternate app stores such as APKpure and APKCombo, often targeting users to spy on their habits and steal data. Kaspersky says that this malware campaign has been live for over 4 years, and is likely the work of the OceanLotus advanced persistent threat (APT) group, thought to be based out of Vietnam. The malware mainly targets users in Vietnam, Bangladesh, Indonesia, and India to collect information such as location data, call logs and contacts, and can even monitor SMS activity, and read the phone’s OS version, model and list of installed applications. While it has not been seen in the US or Europe, it could easily appear on the shores of either.

This campaign was discovered after Kaspersky came across a Dr Web report from 2019 concerning a Play Store app that came with a backdoor allowing a Trojan to install malware and exfiltrate data from the device. The Russian security firm found traits of malware in multiple applications distributed via the Play Store. These apps are said to come with a high level of encryption and were more complex than most other malware used by cyber thugs to steal personal and financial data. “PhantomLance has been going on for over five years and the threat actors managed to bypass the app stores’ filters several times, using advanced techniques to achieve their goals,” said Kaspersky researcher Alexey Firsh.

Global CyberSecurity Report

According to the report, the “the threat actor was able to download and execute various malicious payloads, and thus adapt the payload that would be suitable to the specific device environment, such as the Android version and installed apps.”

“This way, the actor was able to avoid overloading the application with unnecessary features and at the same time gather the desired information.” It further adds. The hackers would first upload a clean copy of an application on the Play Store and other app repositories. Once the application was approved, the follow-up versions contained malicious payloads or requisite codes to install apps in the background on the compromised device.

Global CyberSecurity Report

At a time when remote work is becoming universal and the strain on Security Operations, especially in healthcare and critical industries, has never been higher, ransomware actors are unrelenting, continuing their normal operations. Multiple ransomware groups that have been accumulating access and maintaining persistence on target networks for several months activated dozens of ransomware deployments in the first two weeks of April 2020. So far the attacks have affected aid organizations, medical billing companies, manufacturing, transport, government institutions, and educational software providers, showing that these ransomware groups give little regard to the critical services they impact, global crisis notwithstanding. These attacks, however, are not limited to critical services, so organizations should be vigilant for signs of compromise.

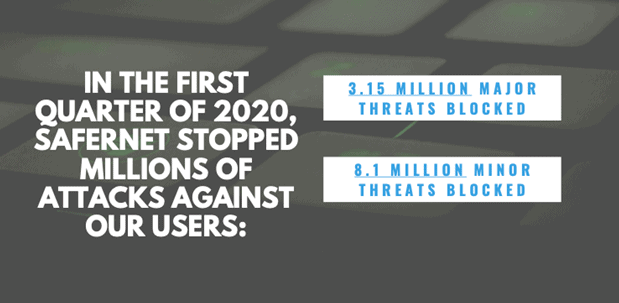
Of the major threats blocked this year by SaferNet,
approximately 165,000 were ransomware related
Global CyberSecurity Report

The ransomware deployments in this two-week period appear to cause a slight uptick in the volume of ransomware attacks. However, Microsoft security intelligence as well as forensic data from relevant incident response engagements by Microsoft Detection and Response Team (DART) showed that many of the compromises that enabled these attacks occurred earlier. Using an attack pattern typical of human-operated ransomware campaigns, attackers have compromised target networks for several months beginning earlier this year and have been waiting to monetize their attacks by deploying ransomware when they would see the most financial gain. Many of these attacks started with the exploitation of vulnerable internet-facing network devices; others used brute force to compromise RDP servers. The attacks delivered a wide range of payloads, but they all used the same techniques observed in human-operated ransomware campaigns: credential theft and lateral movement, culminating in the deployment of a ransomware payload of the attacker’s choice..

Global CyberSecurity Report

On April 20, 2020, more than 267 million Facebook profiles were found listed for sale on the Dark Web — for only $600. Reports link these profiles back to the Facebook data leak discovered in December 2019, and possibly others. Researchers are still uncertain how this data was first exposed but have noted that 16.8 million of the Facebook profiles now include more data than was disclosed originally, including account holder’s email address, birth date, and gender. These expanded profiles may be a result of multiple breaches and leaks of Facebook data being cobbled together to round out Facebook user information, adding more value for cyberthieves selling it on the Dark Web, and increasing account holders’ risk of identity theft.

The type of data included in Facebook’s recent leaks — email, phone number, birth date, and account login information — is commonly used for credential stuffing and phishing attacks once discovered by fraudsters or purchased on the Dark Web. It is essential to safeguard your information by updating your passwords, making sure you do not use the same password on multiple accounts, and turn on two-factor authentication to further protect yourself from account takeover attacks. Armed with your email and phone number, scammers can easily craft spear phishing or SMS attacks to steal more personal information or inject malware into your device.

Global CyberSecurity Report

On Wednesday, the video conferencing service Zoom announced a number of small but needed security improvements. As Zoom usage has increased during the pandemic, so has scrutiny of the service’s security and privacy offerings. This week’s announcement of incremental improvements is part of a 90-day plan the company announced to overhaul its practices. One change is that Zoom will now offer AES 256 encryption on all meetings, meaning data will be encrypted with a 256-bit key. Zoom previously used AES 128, a reasonable option, but a controversial one in Zoom’s case, because the company claimed in documentation and marketing materials that it used AES 256 all along.

Global CyberSecurity Report Global CyberSecurity Report

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are fully protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories. Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all size of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Protect your business or family with SaferNet today and have peace of mind that your online and network safety is assured.

Digital Herd Immunity

Internet Security shouldn’t be a secret…

As SaferNet users, you have empowered yourselves, your families, or your businesses to live in digital freedom, safe from the evils of the Internet. Like a vaccine, your SaferNet service protects your devices against malicious attacks; malware, phishing attempts, trojans, spyware, and more.

During this pandemic, we have seen the best of humanity come to the forefront; Neighbors helping neighbors, friends reaching out to others in need, the community supporting their healthcare workers – social distancing is bringing people together by keeping them apart. While we as people try to slow the spread of a physical virus, the spread of digital viruses has increased dramatically.

digital herd immunity

Examining reports from other security professionals, and monitoring our own servers, we have seen an alarming rise in cyberattacks over the course of the last few weeks. With more people at home and online, hackers and digital bad actors have ramped up their productivity to snare unsuspecting individuals, families and businesses who have moved to a new work-from-home reality.

Naturally, if you feel safe, your objective should be to help everyone else feel safe. If you are protected, your objective should be to get others protected too. Internet security shouldn’t be a secret, and so your SaferNet service shouldn’t be either. By telling friends, family, or small businesses you’re in contact with about SaferNet, you can help build Digital Herd Immunity against online viruses. Many SaferNet users have already made their local internet communities safer by just talking about their service, while others have signed up to our referral program to make generous commissions from educating others on the threats of cybersecurity.

digital herd immunity

Hearing about friends and families being hacked, having their information stolen, or having their devices get damaged is never good. Together, we can put an end to this. Together, we can be stronger against the spread of a digital pandemic.