Acquisition of VPNs by Big Tech Raises Privacy Concerns

“If U.S. intelligence experts believe Beijing and Moscow are leveraging Chinese and Russian-made technology to surveil Americans, surely DHS should also be concerned about Americans sending their web browsing data directly to China and Russia.”

These were the words of Senators Marco Rubio (R-FL) and Ron Wyden (D-OR) to Christopher Krebs, Director at the Cybersecurity and Infrastructure Security Agency (CISA) in a bipartisan investigation into the extent to which VPN companies are being used by Russia and China as surveillance tools to spy on Federal employees.

The investigation was not the first of its kind – a similar examination took place in 2019, and DHS issued a ban of Kaspersky products on Federal IT systems.

Both investigations were carried out to protect federal systems, but such findings must be extended to ordinary American citizens also.

The concern that VPN services have been funneling user data to foreign countries via a parent company has been present for a number of years, but the acquisition of ExpressVPN by Kape Technologies PLC has renewed those fears once more.

ExpressVPN has been a leader in the Virtual Private Network sector for several years and has over three million subscribers. The acquisition shed some light on their finances, showing that they generated “revenues of approximately $279.4 million in 2020, up 37% from 2019”. They have championed data privacy since their launch, often appearing in collaboration with other privacy-oriented services like DuckDuckGo.

ExpressVPN went a step further, establishing their HQ in the British Virgin Isles, and establishing their own protocol named Lightway to ensure user privacy.

Kape Technologies bought the company last week for $936 million, which makes it the most expensive acquisition in the history of the VPN industry.

The acquisition marks the fourth time Kape has purchased a VPN. 2017, it acquired Romanian VPN provider CyberGhost VPN, and in October 2018, it acquired the German-based VPN provider ZenMate.
Acquisitions are not cause for concern by themselves, however, Kape’s past certainly casts a shadow over the deal. Up until March 2018, Kape was known as Crossrider. The name change was due to gaining a shady reputation – Crossrider was branded as Adware by Symantec’s Security Center. The program replaced ads with its own in browsers, collected personal data, and connected to the Crossrider domain.

Malwarebytes had a similar outlook warning users that the Crossrider program was involved in browser hijacking, malicious software bundlers, adware, and other monetizing methods.

There are other factors to consider in the Kape/Crossrider story. Its founder and CEO for a number of years was part Unit 8200, an elite Israeli government body similar to the NSA. Its main investor was Teddy Sagi, whose name is included in the Panama Papers.

With details such as these, users of ExpressVPN who subscribed out of privacy concerns have a right to worry.

ExpressVPN is not the first VPN company to be acquired by a larger company with a shady or undesirable background. A study from VPNpro showed that 101 companies belong to just 23 companies, many of which are based in countries with poor privacy regulations.

The study highlighted that nearly 33% of popular VPNs are owned by Chinese companies, or run by Chinese nationals. This means user data is likely open to Chinese authorities, confirming US Senators’ fears of American data falling into Chinese or Russian hands. China is the world leader in online surveillance, which is the very thing VPNs purport
to protect.

Not only are VPN providers in foreign nations obliged to hand over data to Government, it is also possible that they’re selling the information to their respective governments.

VPN users are at risk from these parents companies, risking their data being sold privately to other companies or being handed over to foreign governments. Based on research by VPNPro, we’ll look at some other companies besides Kape that own large slices of the VPN cake.

j2 Global – 13 VPN services
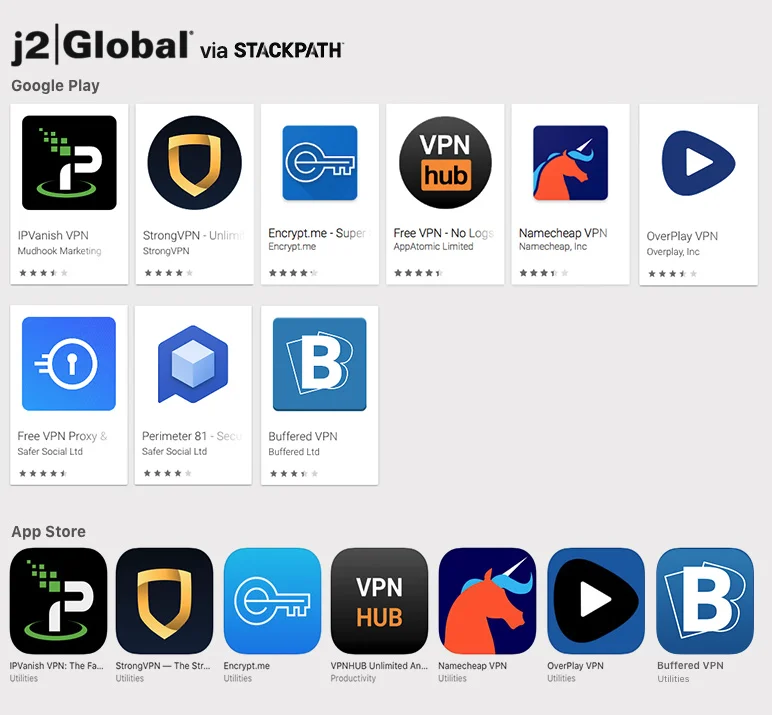
j2 Global, which also owns tech publication PCMag (who coincidentally do VPN reviews) recently acquired StackPath’s VPN products. StackPath states that they’re “an American content delivery network, cloud service, and web application firewall provider.” To branch out, StackPath bought Highwinds in 2017, which included IPVanish, StrongVPN, and Encrypt.me (formerly Cloak).

j2 Global is connected to many more VPNs than its website claims. On top of IPVanish, StrongVPN, and Encrypt.me, it also owns SaferVPN and OverPlay VPN through its subsidiary NetProtect.

The company also owns WLVPN.com, a white-label service that offers VPN infrastructure and strategy services.

With a white-label, VPN providers can buy software development kits (SDKs) from WLVPN to help them develop their VPN applications and features.

NetProtect claims that more than 100 businesses use WLVPN’s infrastructure and tools to power their VPNs, including StrongVPN, OverPlay VPN, Encrypt.me, and VPNhub, Pornhub’s VPN service. j2 Global’s reach should not be understated, and given that they own the largest publication that does VPN reviews it should be cause for concern.

AnchorFree – 10 VPN services
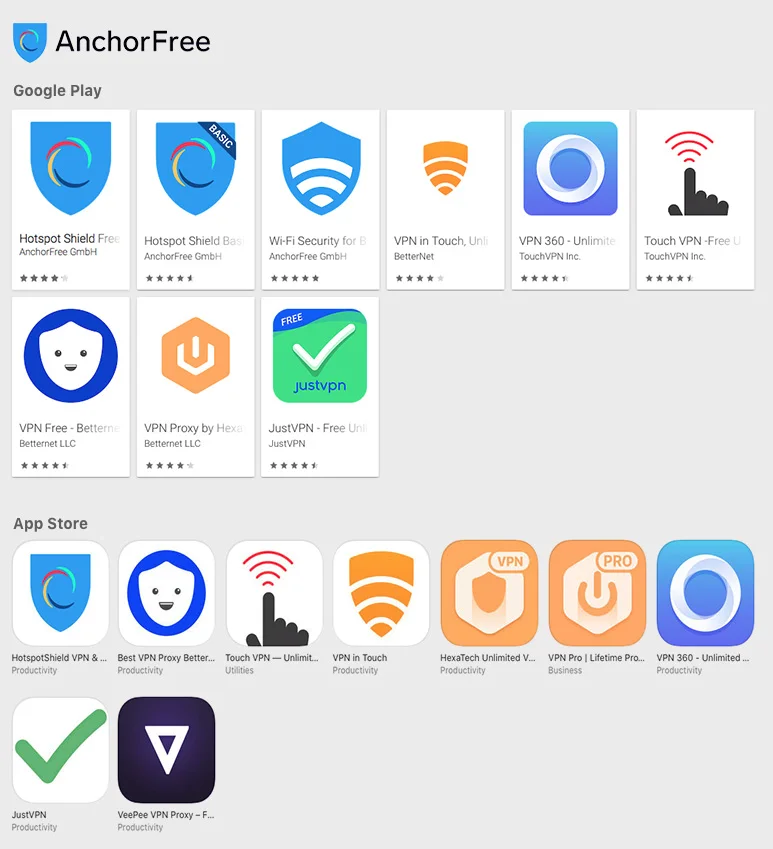
AnchorFree is a veteran on the VPN scene, first appearing in 2008 with HotSpotShield. Though a popular VPN, HotSpotShield was mired in controversy and rumors that they were selling user data.

In August 2017, the Center for Democracy and Technology (CDT) issued an open complaint to the Federal Trade Commission which they state “concerns undisclosed and unclear data sharing and traffic redirection occurring in Hotspot Shield Free VPN that should be considered unfair and deceptive trade practices under Section 5 of the FTC Act.” CDT “partnered with researchers at Carnegie Mellon University to analyze the app and the service and found ‘undisclosed data sharing practices’ with advertising networks.”

Though mostly known for HotSpotShield, AnchorFree has been quietly buying up a number of VPN services.

In February 2015, AnchorFree acquired JustVPN and TouchVPN. JustVPN has just one VPN product: an Android app called “JustVPN – Free Unlimited VPN & Proxy.”

TouchVPN has three unique apps. Two are for Android (Touch VPN, VPN 360), and three are for iOS: VPN 360, Touch VPN, VeePee VPN Proxy.

In November 2016, Betternet Technologies was acquired by AnchorFree. Betternet creates the following mobile apps:

Android:

  • VPN Free – Betternet Hotspot VPN & Private Browser
  • VPN Proxy by HexaTech
  • VPN in Touch (developer listed as just “Betternet”)


iOS:

  • Best VPN Proxy Betternet
  • HexaTech Unlimited VPN
  • VPN in Touch
  • VPN Pro | Lifetime Proxy & Best VPN by Betternet

Gaditek – 7 VPN services
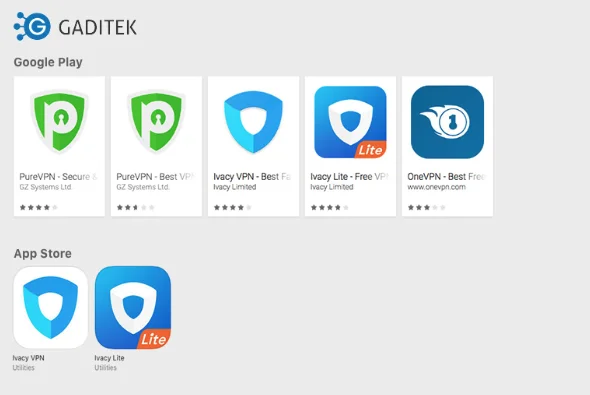
Gaditek is a Pakistan-based company that owns PureVPN, Ivacy, and Unblock – a newer VPN and proxy product. Pakistan’s own privacy laws are not particularly rigid, and the country has often come under fire from international NGOs. Freedom House’s annual internet freedom report has repeatedly given Pakistan a rating of “not free.”

Pakistan practices heavy online censorship. The government blocks residents from accessing websites and social media platforms that express dissenting political opinions. Authorities also frequently disable mobile internet access during large protests or other politically sensitive events.

There are several cases of people being sentenced to death for their social media activity. Some reports suggest that Pakistan has begun targeting human rights defenders with invasive cyberattacks.

Pakistani law also makes it extremely easy for authorities to obtain a warrant to access citizens’ private data for almost any reason. This begs the question, how much control does the Pakistan government have over Gaditek?

The employees of Gaditek/PureVPN have also been connected to the following VPN review sites:

  • vpnranks.com
  • bestvpnservice.com
  • kodivpn.co
  • bestvpn.co (previously bestvpnprovider.com)
  • usavpn.com

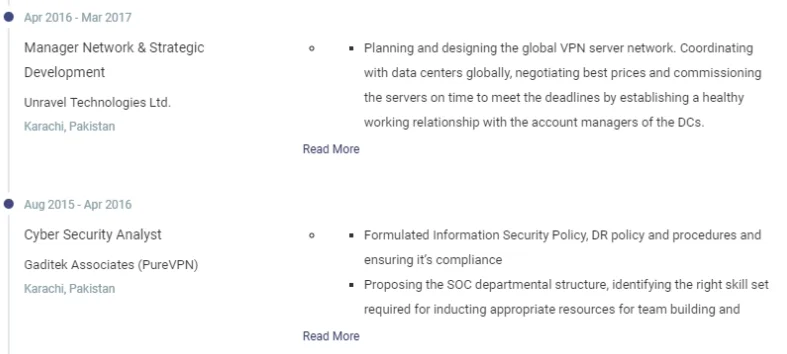
Some employees of PureVPN and Gaditek also worked for another VPN provider called OneVPN, which is owned by Unravel Technologies.

Unravel is supposed to be based in Hong Kong, but like PureVPN, its base is actually in Karachi, Pakistan. Muhammad Fahad’s job profile shows him working at first Gaditek then Unravel, both in Karachi:
PureVPN, IvacyVPN, and vpnranks.com all share the same registration address in Singapore. The next company on this list – Innovative Connecting – also has the same address.

Innovative Connecting – 10 VPN services
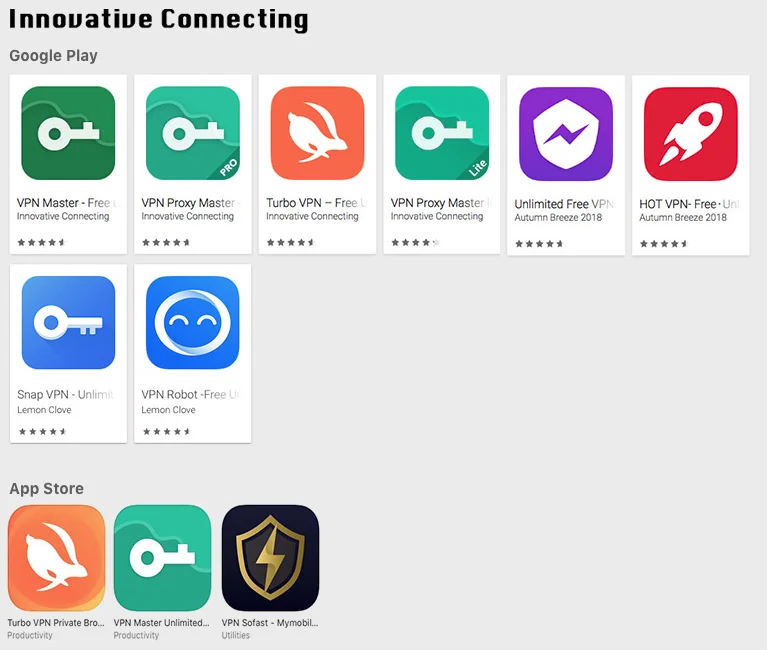
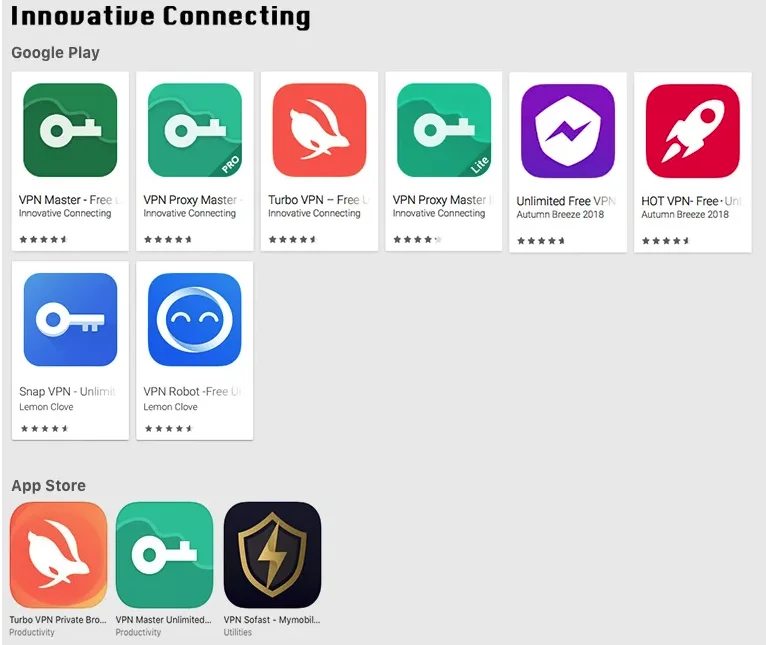
Innovative Connecting is a young Singapore-based tech company that specializes in mobile app development. This Android developer directly makes TurboVPN, VPN Master, VPN Proxy Master Pro, and VPN Proxy Master Lite. It also develops the iOS app VPN Sofast – Mymobilesecure.

Innovative Connecting has been connected with Lemon Clove as well (in addition to a third company, ALL Connected Co. Ltd). Lemon Clove makes the VPN apps Snap VPN and VPN Robot.

Lemon Clove and Innovative Connecting both have the same secretary and key addresses. Additionally, the company’s LinkedIn page says that its product development team is actually based in China. Director Danian “Danny” Chen is a Chinese national.

When researchers studied the APK files for the three companies, they found the API calls going to the same domains
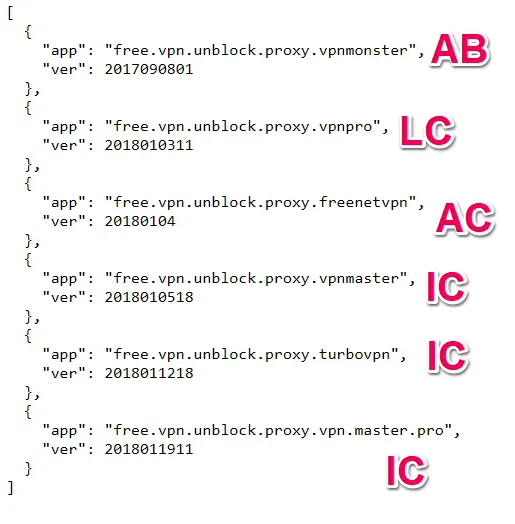
While it is clear Innovative are trying to hide their reach, they are behind many more VPNs than they claim to be.

SuperSoftTech – 3 VPN services
The company developers 3 apps; SuperVPN, VPN Payment Tool, and LinkVPN. While the apps are officially owned by the SuperSoftTech company based in Singapore, it actually belongs to the independent app publisher Jinrong Zheng – most likely a Chinese national based in Beijing.

The contact email address on the Play store ([email protected]) links to a Chinese address in Beijing. Jinrong Zheng has released several apps (mostly games) that almost all start with the prefix “Super.”

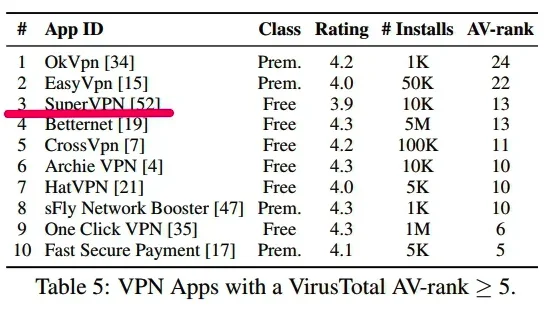
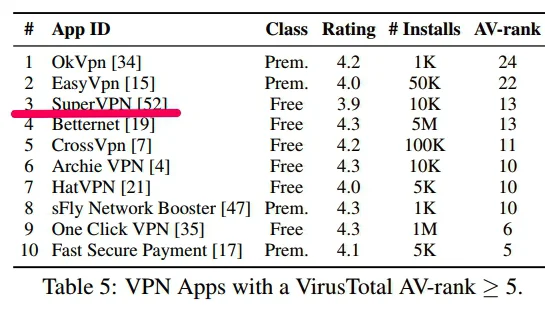
SuperVPN has been ranked the #3 most malware-rigged VPN app in a 2016 Australian research by Csiro:
Other Companies That Own Several VPNs

  • Hotspot VPN (5 apps): Director Zhu Jianpeng has a residential address in Heibei Province in China
  • Hi Security (3 VPN apps): the VPN apps are part of Shenzhen HAWK Internet, a subsidiary of the Chinese major company TCL Corporation
  • Newbreed Network Pte.Ltd (6 apps): While it has a Singapore address, the websites for its VPN apps SGreen VPN and NodeVPN are completely in Chinese, while NodeVPN’s site lists the People’s Republic of China as its location.
 

A Risk-Free VPN and the Future of the Industry

It is clear that the VPN industry, initially thought to be a bastion of privacy and security, has become controlled by mendacious parent companies, holding companies, and megacorporations that are willing to sell out the average user to governments or advertisers.

In an age where living without a VPN leaves you and your data entirely exposed, it is nothing short of tragic that users wishing to escape into the safe harbor of a trusted VPN have their fears turned against them.

There are always independent VPN services fighting the privacy fight in earnest, without turning on users and seeing them as the product to sell.

When considering a VPN service, consumers now must be well-informed or face the risks associated with choosing an untrustworthy provider.

Here are some factors those who are searching for a VPN should keep in mind:

  • Independence; is the service owned by another company who themselves own a number of other VPN services?
  • Data Limits
  • Speed and throttling
  • Price; the majority of ‘Free’ VPNs are expected to sell your data
  • Security
  • Company headquarters – Is the company based in a country with modern privacy laws?
  • Privacy; what kind of logs are kept?
  • Customer support

At SaferNet, we offer a competitive VPN for individuals, families, and businesses that ticks all these boxes and more.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

A Look At VPNs Covertly Operating From Within Chinese Boarders

VPNs (Virtual Private Networks) are a significant factor in ensuring a safe connection and privacy when using the internet. In an age where consumer privacy is not given much priority, the number of VPNs available and VPN users signing up for them has exploded. The competition for providers is fierce, and a handful of companies control the majority of the market.

The underlying technology that makes up a VPN is sophisticated, involving information encryption which is fed through the VPN companies’ servers, and sent to the wider internet. Thus, there is a degree of trust required between the VPN user and the company they decide to sign up with.

Of course, there is no VPN company in operation out there that will admit that they’re untrustworthy, or that they sell data, or that they have a checkered history when it comes to privacy. In fact, many VPN providers will go to great lengths to conceal that they’re owned by other companies which may have come under scrutiny in the past.

VPN companies will go to even greater lengths to conceal the fact that they may be owned by a company in a different country – Specifically one in China. In a recent report by VPNPro, it was revealed that a third of major VPN providers are either owned by Chinese companies directly or are owned by proxy, via shell companies and Chinese students in C-level positions.

In short, many VPN providers are not being transparent with their userbase.

The interference of the Chinese Communist Party in business affairs is no secret, with business operating in China as a sort of State-controlled quasi-capitalism system. Not only does the CCP have absolute reach into the business dealings of a company operating from within their borders, a VPN owned by a Chinese company means that the Chinese government can legally demand users’ data.

This has not gone unnoticed by the government of the United States. A recent bipartisan investigation was taken up by Senators Marco Rubio (R-FL) and Ron Wyden (D-OR) into the extent to which VPN companies are being used by Russia and China as surveillance tools to spy on Federal employees. In the report, the Senators said, “If U.S. intelligence experts believe Beijing and Moscow are leveraging Chinese and Russian-made technology to surveil Americans, surely DHS should also be concerned about Americans sending their web browsing data directly to China and Russia.”

The situation is grave, and it’s getting much worse as more popular VPN providers are being bought up Chinese firms. In addition, VPNs with Chinese developers have begun to flood the US market. These VPNs provide a direct line of information about American citizens straight back to Chinese authorities.

The VPN market, once a stronghold of privacy, has become a data-driven arms race as corporations use providers as funnels for information. In this post, we’ll look at some of the largest VPN services coming out of China, which should be avoided at all costs.

Innovative Connecting

Innovating Connecting (IC) is a significant player in the VPN market, owning a total of ten different VPNs. The company is also known as ALL Connected (AC), and on their website they claim to be based out of Singapore. However, digging into the company via LinkedIn reveals that the development unit is based in China. The director at the company, Danian “Danny” Chen, is a Chinese national.

Looking deeper into the code of several VPNs and company addresses, one can learn that IC and AC share the same address and similar code as Lemon Clove (LC), yet another VPN company that develops VPN Robot and SnapVPN. Lastly, LC themselves go by another name, Autumn Breeze (AB). AB develops Hot VPN and Unlimited Free VPN Monster.

Of the ten, here are the 5 most popular, with reviews from Techshielder:

Turbo VPN
Despite its mobile applications having numerous downloads, this is not a safe VPN to use. Turbo VPN is an example of fame not equating quality. Stay away from this VPN if you value your privacy, as it will release your information if requested by the government. Despite its no-log policy, it collects data regarding where you’re connecting from, where you’re connecting to, the size of data, and other analytics data. It is also full of unwanted ads, risky permissions, malware, and DNS leaks. In summary, using Turbo VPN is a risk that you might not be willing to take.

VPN Proxy Master
Here is another famous free VPN service provider. The problem with most free VPNs is that since they are not making any money from subscriptions to their service, they look for alternative ways to make do. It has advertising partners like Facebook, UnityAd, Vungle, and AdMob. VPN Proxy Master has a nosy logging policy and lacks extensive security features. It is better to find an excellent alternative VPN if you are not a fan of these features.

Solo VPN
Minor security features, nosy logging policy, no torrenting, lack of popular streaming support, and aggressive ads are features of this mobile VPN application. Although it uses strong encryption to protect your data, it still does not guarantee your privacy.

Unlimited Free VPN Monster
This Android-only VPN service provider’s free version will expose you to aggressive ads. It lacks essential security features and doesn’t seem to offer any information about the type of encryption it uses. Although it is clear about the data it collects, it has not been transparent about its owners and location. The lack of transparency is enough reason to avoid Unlimited Free VPN Monster.

IC is shrouded in mystery, has awful business practices, and isn’t being transparent with users. Despite this, their VPNs are popular. It is advisable to stay away from their applications.

SuperSoftTech


Similar to Innovative Connecting, SuperSoftTech operates officially from Singapore. The company however belongs to Jinrong Zheng, a Chinese citizen living in Beijing. Applications created by Zheng include SuperVPNVPN Payment Tool, and LinkVPN.

SuperVPN
SuperVPN is one of the most popular VPNs worldwide, with over a hundred million downloads on Google Play Store. It has the same privacy policy as LinkVPN, which is from the same developer. Its privacy policy gives hints that it might oblige if a superior authority requests your data because it scans IPs against a blacklist.

SuperVPN also stores data in the US and UK according to its privacy policy; however, it is unclear what data this VPN collects and stores. Since users don’t require an account to use SuperVPN, it is confusing why there is a need to store any user data. Although this application has the necessary security protocols to keep you secure, it requests unnecessary permissions from your device. Accepting some of these permissions can leave your data vulnerable.

Despite its popularity, SuperVPN is mired in controversy and has been accused of popping unwanted ads and actually infecting the user with malware. SuperVPN has been ranked the #3 most malware-rigged VPN app in a 2016 Australian research by Csiro:

Other Chinese Companies That Own Or Develop VPNs

Owning over a third of the market, there are a number of other Chinese firms that operate or develop VPNs. Here are some of them:

Newbreed Network
Newbreed Network has about six VPN applications to its name. It claims to operate in Singapore, but the websites of a couple of its VPN applications are in Chinese. VPN Green, SGreen, MasterVPN, NodeVPN, TXVPN, and AirGO Fast are applications with links to Newbreed Network.

Hotspot VPN
The director of Hotspot VPN is Chinese and is resident in China. VPN applications include Free VPN, Hotspot VPN, Secure VPN, and Easy VPN.

Hi Security
Hi Security holds three VPNs: Hi VPN Free, Hi VPN Pro, and Net Master. These applications are part of Shenzhen HAWK Internet, a company under TCL Corporation, a notable Chinese company.

LEILEI
LEILEI owns Yunfan VPN and Bit VPN.

A Risk-Free VPN and the Future of the Industry

It is clear that the VPN industry, initially thought to be a bastion of privacy and security, has become controlled by mendacious parent companies, holding companies, and megacorporations that are willing to sell out the average user to governments or advertisers.

In an age where living without a VPN leaves you and your data entirely exposed, it is nothing short of tragic that users wishing to escape into the safe harbor of a trusted VPN have their fears turned against them.

There are always independent VPN services fighting the privacy fight in earnest, without turning on users and seeing them as the product to sell.

When considering a VPN service, consumers now must be well-informed or face the risks associated with choosing an untrustworthy provider.

Here are some factors those who are searching for a VPN should keep in mind:

  • Independence; is the service owned by another company who themselves own a number of other VPN services?
  • Data Limits
  • Speed and throttling
  • Price; the majority of ‘Free’ VPNs are expected to sell your data
  • Security
  • Company headquarters – Is the company based in a country with modern privacy laws?
  • Privacy; what kind of logs are kept?
  • Customer support

At SaferNet, we offer a competitive VPN for individuals, families, and businesses that ticks all these boxes and more.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

VPNs based in Pakistan

VPNs (Virtual Private Networks) are a significant factor in ensuring a safe connection and privacy when using the internet. In an age where consumer privacy is not given much priority, the number of VPNs available and VPN users signing up for them has exploded. The competition for providers is fierce, and a handful of companies control the majority of the market.

The underlying technology that makes up a VPN is sophisticated, involving information encryption which is fed through the VPN companies’ servers, and sent to the wider internet. Thus, there is a degree of trust required between the VPN user and the company they decide to sign up with.

Of course, there is no VPN company in operation out there that will admit that they’re untrustworthy, or that they sell data, or that they have a checkered history when it comes to privacy. In fact, many VPN providers will go to great lengths to conceal that they’re owned by other companies which may have come other scrutiny in the past.

Recently, SaferNet has reported on the fact that many VPN companies go to great lengths to conceal who truly owns them. Aside from megacorporations playing a part, one of the most notable owners is China, owning a third of all major VPNs through various parent companies. However, another big player in this field is Pakistan, and a company named Gaditek.

This is yet another example of VPN providers not being transparent with their userbase.

Human rights and internet censorship in Pakistan are appalling. Freedom House’s annual internet freedom report has repeatedly given Pakistan a rating of “not free.” due to its actions against citizens and journalists. The Pakistan government practices and the government blocks citizens from accessing websites and social media platforms that express dissenting political opinions.

During large protests and politically sensitive events, authorities often disable mobile internet around the area the events take place in.

Worst of all, there are several cases of people being sentenced to death for their social media activity. Some reports suggest that Pakistan has begun targeting human rights defenders with invasive cyberattacks. The government will often state these are issues of ‘national security’, yet these decisions receive a lot of international criticism.

Pakistani laws and the VPN ethos do not mix. The government enforces strict data retention laws and requires ISPs to keep communication logs for a minimum of one year, or longer if requested by the government. It is also extremely easy for authorities to obtain a warrant to access citizens’ private data for almost any reason. This means that a VPN offers virtually no protection from the Pakistani government.

Gaditek concealing VPN Services

Note: The investigation into Gaditek was initially reported on by VPNPro

Gaditek has a global reach, with 7 VPNs that are popular in Pakistan but also worldwide. While they may promise their users in Pakistan privacy, this is impossible within the laws of the country; something Gaditek isn’t upfront about. From their headquarters in Karachi, Gaditek has deployed several VPNs, the most popular being PureVPN, Ivacy, and unblock. They refer to themselves on their website as “a human-centric New Age company.”

As well as being at the behest of the Pakistani government, Gaditek employs a number of shady marketing practices.

The employees of Gaditek/PureVPN have been connected to the following VPN review sites:

  • vpnranks.com
  • bestvpnservice.com
  • kodivpn.co
  • bestvpn.co (previously bestvpnprovider.com)
  • usavpn.com

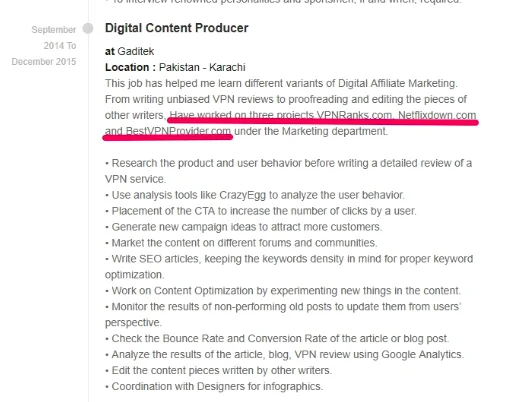
This is a profile from Humayoun Khan, who worked at Gaditek from 2014-2015 and wrote “unbiased VPN reviews” for vpnranks.com, netflixdown.com, and bestvpnprovider.com:

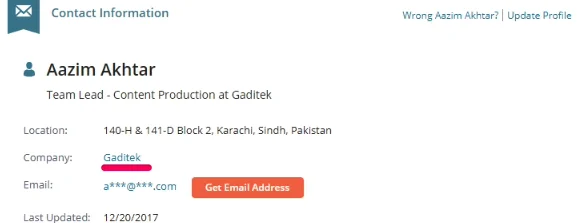
Additionally, Aazim Akhtar is listed as the Senior Editor for vpnranks.com, but on Zoominfo.com, he’s listed as working at Gaditek as their Team Lead for Content Production:

Vpnranks is one of the most popular VPN ranking websites in the world, with 2.5 million monthly visitors. It is now believed that the website is a front for Gaditek to push their product.

Furthermore, an investigation by VPNPro showed that some employees of PureVPN and Gaditek also worked for another VPN provider called OneVPN, which is owned by Unravel Technologies.

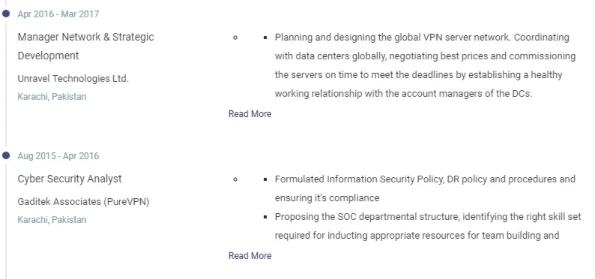
Unravel is supposed to be based in Hong Kong, but like PureVPN, its base is actually in Karachi, Pakistan. Muhammad Fahad’s job profile shows him working at first Gaditek then Unravel, both in Karachi:

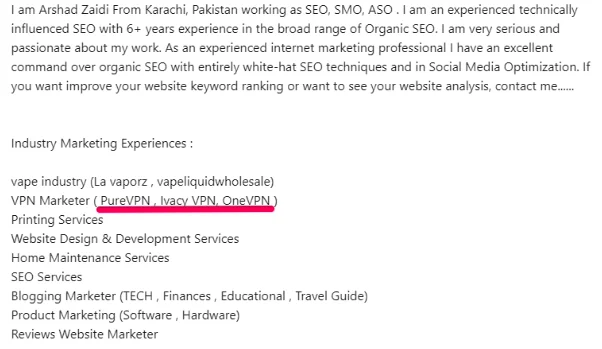
Then there’s Ashad Zaid’s LinkedIn profile that shows he only worked at Gaditek from 2015-2016, but not Unravel Technologies or OneVPN, but still lists OneVPN (along with Gaditek products PureVPN and Ivacy) as some of the projects he’s worked on:

By this, it would seem that Gaditek also owns OneVPN, but is not reported by them. While the Hong Kong address for Unravel suggests a Chinese connection, there is greater evidence else to show an even stronger connection.

PureVPN, IvacyVPN, and vpnranks.com all share the same registration address in Singapore. Yesterday, SaferNet reported on VPNs secretly operating from China. One of the largest companies that do this is name Innovative Connecting (IC).

IC themselves are a whole other story and own several companies they haven’t been transparent about. IC’s registered address is the same as PureVPN, IvacyVPN, and vpnranks.com.

This suggests that there is an incredibly strong link between Gaditek and IC, with the latter possibly being a parent company to the former. Either way, it’s clear that neither company is being quite honest, and that is the last thing a VPN user wants from a provider

A Risk-Free VPN and the Future of the Industry

It is clear that the VPN industry, initially thought to be a bastion of privacy and security, has become controlled by mendacious parent companies, holding companies, and megacorporations that are willing to sell out the average user to governments or advertisers.

In an age where living without a VPN leaves you and your data entirely exposed, it is nothing short of tragic that users wishing to escape into the safe harbor of a trusted VPN have their fears turned against them.

There are always independent VPN services fighting the privacy fight in earnest, without turning on users and seeing them as the product to sell.

When considering a VPN service, consumers now must be well-informed or face the risks associated with choosing an untrustworthy provider.

Here are some factors those who are searching for a VPN should keep in mind:

  • Independence; is the service owned by another company who themselves own a number of other VPN services?
  • Data Limits
  • Speed and throttling
  • Price; the majority of ‘Free’ VPNs are expected to sell your data
  • Security
  • Company headquarters – Is the company based in a country with modern privacy laws?
  • Privacy; what kind of logs are kept?
  • Customer support

At SaferNet, we offer a competitive VPN for individuals, families, and businesses that ticks all these boxes and more.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Top 5 Secure VPNs That Are Focused on Privacy

This week, SaferNet has looked at the corruption within the VPN industry. Though the core ethos of the mark focuses on the privacy of its users, we have learned that this is rarely the case. Instead, many VPN providers are owned by data-greedy corporations who sell their users out or even worse are owned by companies based within countries with shakey privacy laws. This often means that such companies are at the mercy of their governments, and user data may freely be passed around with the customer’s knowledge or permission.

It can be easy to lose heart in the industry. In one sense, you are completely vulnerable without a VPN. But seemingly signing up for a VPN can leave you in a much worse position. Despite how bleak the outlook is, there are still several VPN providers fighting the good fight and putting user privacy as their number one priority.

When considering a VPN service, consumers now must be well-informed or face the risks associated with choosing an untrustworthy provider.

Here are some factors those who are searching for a VPN should keep in mind:

  • Independence; is the service owned by another company who themselves own a number of other VPN services?
  • Data Limits
  • Speed and throttling
  • Price; the majority of ‘Free’ VPNs are expected to sell your data
  • Security
  • Company headquarters – Is the company based in a country with modern privacy laws?
  • Privacy; what kind of logs are kept?

In this post, we’ll look at the top 5 VPNs that put emphasis on privacy and aren’t aiming to sell out their user base. Many of the reviews found here can be seen in greater detail on VPNPro.

VpyrVPN


VyprVPN is one of the best overall VPNs on the market. It offers great privacy and security without sacrificing speed. Implementing WireGuard protocol means that we should see this service among the fastest very soon. This also means that you’re getting great P2P protection without sacrificing speed.

VyprVPN is the best for those living under repressive regimes, such as Russia or North Korea. Even the infamous Great Firewall of China is no match to this VPN.

This VPN has user-friendly apps for all popular platforms, as well as some less popular ones. It will help you get past geo-blocking and watch multiple streaming platforms, Netflix included.

VyprVPN is based in Switzerland, a country known for its strong privacy laws. As such, there has never been any need for the VPN provider to retain logs of user data. However, until late in 2018, VyprVPN company policy was to record some identifying metadata including “the user’s source IP address, the VyprVPN IP address used by the user, connection start and stop time and total number of bytes used.”

Although IP addresses aren’t typically considered Personally Identifiable Information (PII), they can and have been used to identify individuals through their Internet Service Provider (ISP). As such, we try to avoid recommending providers that retain such logs.

Thankfully, VpyrVPN overhauled its policy in 2018 and now keeps no logs whatsoever. The company even subjected itself to an independent audit to prove that no logs are maintained.

ProtonVPN

ProtonVPN is a highly regarded VPN brand from the same CERN scientists who gave us ProtonMail. It has received widespread acclaim for its content protection measures and privacy policy.

ProtonVPN has set out to offer the world a VPN that is secure, not funded through malicious means, and not limited in terms of bandwidth or amount of data transferred.

ProtonVPN is very committed to robust online security and privacy. Security-wise, it’s incredibly safe and is a surefire choice for protecting your digital assets. From hiding your IP address and ensuring your anonymity online, to torrenting safely and avoiding online censorship, this VPN service is pretty much as good as it gets.

ProtonVPN is suitable for security-first users who are willing to wait when this service grows their server and location numbers. It is a hugely ambitious project, lead by the CERN employees, and already the best choice for those who want a free VPN.

SurfShark VPN

Since its launch in 2018, Surfshark has earned the consumer’s trust and became one of the top overall VPNs. This wasn’t just about excellent speed or top-notch security and privacy. The biggest argument for Surfshark VPN was getting all that for a low price.

Operating from the British Virgin Islands, this provider has set a strict standard upon itself. It has a no-logs policy and stays away from the Five Eyes surveillance alliance. Additionally, Surfshark uses military-grade encryption and the latest tunneling protocols to protect its users.

With Surfshark VPN, you’ll be able to torrent safely and watch multiple streaming platforms. There more than 3200+ servers in 65+ countries, so if one won’t unblock Netflix, the other will.

NordVPN

With such a great reputation behind it, Nord has become almost synonymous with the name VPN, and it certainly is a contender for the #1 spot.

NordVPN server list is one of the best in the industry. It allows them to provide truly global coverage and reliable connections all over the world. If you don’t have a particular location in mind, this service can automatically select the best server for you based on their loads.

Many VPN services claim to provide complete anonymity on the internet, but only a few can back it up in features and evidence. NordVPN is one of the few, having these security and privacy features:

  • Military-grade encryption
  • Latest tunneling protocols
  • Minimal logging

In October 2019, it came to light that an attacker remotely accessed one of NordVPN’s servers. NordVPN says there is no evidence that the attacker obtained anything significant. We discuss the attack, and its consequences, in much greater detail in a feature article about the breach. The company has since invested significant time and capital into hardening its systems and practices, including the moves to its own server clusters and diskless servers.


SaferNet

SaferNet was established to give VPN users something they didn’t have previously – Choice. It is engineered to allow users set a tailor-made online experience, allowing them to decide what what should and shouldn’t be allowed to access their devices.

Using the same robust encryption and tunneling protocols found in similar VPNs such as NordVPN, as well as a machine-learning driven approach to cybersecurity, SaferNet is one of the few VPNs on the market that can supplement and enchance traditional security products such as Windows Defender.

SaferNet has a unique approach to logging. Because the VPN can be used to monitor family members or an entire office, account administrators can access logs for all devices under their SaferNet account. However, these logs are entirely after a treshhold of entires or when a number of days has passed. In this sense, SaferNet is the only VPN that lets its customers use logs to their benefit before deleting them.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Business Software Solution Hit With BlackMatter Ransomware

BlackMatter Ransomware struck over the weekend, targeting business software solutions provider Marketron. Marketron is a growing business and has more than 6,000 customers in the media industry. It provides cloud-based revenue and traffic management tools for broadcast and media organizations. The company specializes in revenue management and audience engagement, handling advertising revenue of $5 billion every year.

Marketron customers were informed of the BlackMatter Ransomware attack in an email on Sunday night from the company CEO, Jim Howard, who said that “the Russian criminal organization BlackMatter” was responsible for the attack.

The BlackMatter Ransomware gang is seemingly ramping up operations – Last week SaferNet reported on a BlackMatter breach within the NEW Cooperative U.S. farmers organization, which demanded a $5.9 million ransom.

Howard is apologetic in the email to his customers, stating that they are unaware of how the BlackMatter Ransomware gang breached the network, given that Marketron has made significant investments recently in cybersecurity implementations designed to protect from intruders.

“This issue comes despite significant recent investments in separating backup and disaster recovery in different physical and network environments, instituting ‘zero trust’ access management policies, and new security detection and recovery tools”, Howard said in the email.

He went on to state that the company is in contact with both the BlackMatter Ransomware gang and the FBI, and that all efforts are being made to restore systems as soon as possible.

Marketron publically announced the incident this morning, stating that it was dealing with a “cyber event” that disrupted some of its business operations and impacted all its customers.

“Currently, all Marketron services are offline,” the company announced, adding that the attack affected the Marketron Traffic, Visual Traffic Cloud, Exchange, and Advertiser Portal services.

RadioTraffic and RepPak services were still standing but the company took them offline as a precaution. The only platforms that remained online were Pitch, Email Marketing, and Mobile Messaging.

Bo Bandy, VP of Marketing at Marketron, said in the disclosure that third-party forensic investigators were working “to understand the full nature and scope of the event, determine root cause, and to ensure the integrity, safety, and security of our systems and data.”

“We are unable to confirm the root cause of the event at this time and this investigation is very much on-going” Bandy said.

BlackMatter Ransomware is believed to be a rebrand of Darkside Ransomware, which took Colonial Pipeline offline in May.

The gang have been extremely active this month alone and has a gallery of victims including:

  • a wine and spirits company
  • an investment banking services provider in the U.S.
  • a vendor of citrus juicing equipment in Austria
  • a maker of drilling and foundation equipment in Italy
  • Japanese technology giant Olympus
  • a US-based construction company
  • a unified communications company in the UK

BlackMatter Ransomware Analysis

Note: This analysis was carried out by Sophos Labs

The Sophos research is based on a sample of the BlackMatter ransomware, with the SHA-256 hash: 22D7D67C3AF10B1A37F277EBABE2D1EB4FD25AFBD6437D4377400E148BCC08D6.

The operators behind the BlackMatter RaaS have established a presence on the dark web:

The list of sectors and entities this threat actor says it will not attack reflect the recent global incidents involving DarkSide (Colonial Pipeline) and REvil (Kaseya) ransomware, which drew widespread and probably unwelcome attention.

The operators behind BlackMatter claim that their ransomware incorporates the best features of DarkSide, REvil, and LockBit 2.0 ransomware. They also say that while they are closely acquainted with the Darkside operators, they are not the same people – this idea has been contested by researchers.

Below is a short comparison of some of the capabilities seen in the various groups:

When victims are hit with the BlackMatter ransomware and the files on the drives are encrypted, BlackMatter sets a wallpaper that is very similar to DarkSide’s. Also, like DarkSide, this is stored in the same folder on disk (C:\ProgramData), with an identical file size (2,818,366 bytes), image format (.BMP) and image size (1706 x 826 pixels, 16-bit color depth.)

Like DarkSide (and REvil), BlackMatter uses a run-time API that can hinder static analysis of the malware. And like the other two ransomware groups, strings are also encrypted and revealed during runtime. While both of these techniques are common across many recent malware, the way in which the runtime API and string decryption function in BlackMatter is very similar to the functionality seen in DarkSide and REvil.

In another shared similarity with both REvil and Darkside, BlackMatter ransomware stores configuration information in the binary in an encoded format. SophosLabs decoded this and found that BlackMatter ransomware has a similar structure and information stored in the configuration blob, like lists of processes and services to kill, the ransom note, C2 details, directories to avoid etc.

The ransomware can encrypt open (locked) documents. BlackMatter terminates several productivity-related processes before encryption begins:

  • ensvc
  • thebat
  • mydesktopqos
  • xfssvccon
  • firefox
  • infopath
  • winword
  • steam
  • synctime
  • notepad
  • ocomm
  • onenote
  • mspub
  • thunderbird
  • agensvc
  • sql
  • excel
  • powerpnt
  • outlook
  • wordpad
  • dbeng50
  • isqlplussvc
  • sqbcoreservice
  • oracle
  • ocautoupds
  • dbsnmp
  • msaccess
  • tbirdconfig
  • ocssd
  • mydesktopservice
  • visio

The BlackMatter ransomware collects information from victim machines, like hostname, logged in user, operating system, domain name, system type (architecture), language, as well as the size of the disk and available free space.

The analyzed sample sends these details to a remote server hosted on paymenthacks.com. It uses a specific header to post the information.
The BlackMatter ransomware drops a ransom note in user-accessible folders on the disk.


Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

The Republican Governors Association Servers Hit In Data Breach

The Republican Governors Association (RGA) revealed that they were victims of a data breach in notification letters sent last week to members. The data breach occurred during an extension Microsoft Exchange hacking campaign that hit organizations worldwide this year, an incident that uses what is now known as the ProxyLogon exploits.

RGA is a US political organization that providers Republican candidates with the campaign resources needed to get elected as governors across the country.

Following an investigation into a possible data breach which began in March, “RGA determined that the threat actors accessed a small portion of RGA’s email environment between February 2021 and March 2021 and that personal information may have been accessible to the threat actor(s) as a result.”

Though initially, the RGA stated they were not able to discover if any personal information was taken in the data breach, a subsequent “thorough data mining effort to identify potentially impacted individuals” revealed that names, Social Security numbers, and payment card information was exposed in the attack.

RGA discovered that individuals affected by this data breach had their personal information exposed on June 24 and completed its “data mining” efforts on September 1.

“Once potentially impacted individuals were identified, RGA worked to identify addresses and engage a vendor to provide call center, notification, and credit monitoring services,” RGA told impacted individuals in a data breach letter sent on September 15.

“RGA is also offering you two (2) years of complimentary credit monitoring and identity restoration services with Experian. RGA has also notified the Federal Bureau of Investigation, certain state regulators, and the consumer reporting agencies of this incident as required.”

ProxyLogon: Catalyst to the Data Breach

The hacking campaign RGA refers to in its data breach notification letter targeted more than a quarter of a million Microsoft Exchange servers, owned by tens of thousands of organizations around the world.

The attackers exploited four zero-days (collectively known as ProxyLogon) in attacks targeting on-premises Microsoft Exchange servers in indiscriminate attacks against orgs from multiple industry sectors worldwide, with the end goal of stealing sensitive information.

At the time of the attack, Microsoft stated that the Chinese state-sponsored hacking group known as Hafnium was behind some of these attacks.

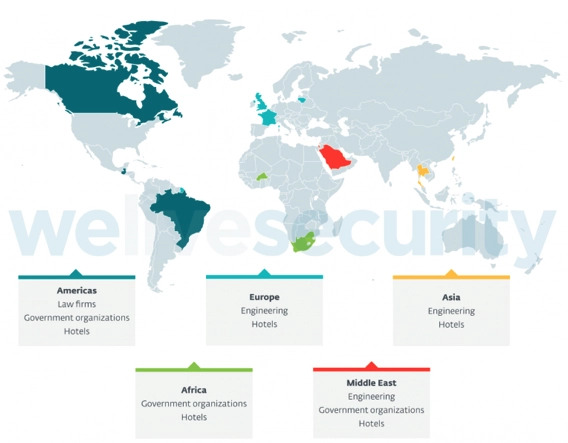
ProxyLogon Attack Map. Source: WeLiveSecurity
 

“Historically, Hafnium primarily targets entities in the United States for the purpose of exfiltrating information from a number of industry sectors, including infectious disease researchers, law firms, higher education institutions, defense contractors, policy think tanks, and NGOs,” Microsoft said.

In July, the company’s attribution was confirmed when the US and allies, including the European Union, the United Kingdom, and NATO, officially blamed China for this widespread Exchange hacking campaign.

Attack History Of The Exploits And Threat Actors That Used Them

The Biden administration attributed “with a high degree of confidence that malicious cyber actors affiliated with PRC’s MSS conducted cyber-espionage operations utilizing the zero-day vulnerabilities in Microsoft Exchange Server disclosed in early March 2021.”

The four zero-days that make ProxyLogon are as follows:

CVE-2021-26855: SERVER-SIDE REQUEST FORGERY
The Server-Side Request Forgery (SSRF) vulnerability provides a remote actor with admin access by sending a specially crafted web request to a vulnerable Exchange Server. The web request contains an XML SOAP payload directed at the Exchange Web Services (EWS) API endpoint. The SOAP request bypasses authentication using specially crafted cookies and allows an unauthenticated, remote actor to execute EWS requests encoded in the XML payload and ultimately perform operations on users’ mailboxes. This vulnerability, combined with the knowledge of a victim’s email address, means the remote actor can exfiltrate all emails from the victim’s Exchange mailbox.

Organizations that received this letter were companies that received threats in August and September of 2020. Analysis of this new wave of ransom letters suggests that the same threat actors from the middle of 2020 are behind these malicious communications.

CVE-2021-26857: REMOTE CODE EXECUTION VULNERABILITY
A post-authentication insecure deserialization vulnerability in the Unified Messaging service of a vulnerable Exchange Server allows commands to be run with SYSTEM account privileges. The SYSTEM account is used by the operating system and services that run under Windows. By default, the SYSTEM account is granted full control permissions to all files. A malicious actor can combine this vulnerability with stolen credentials or with the previously mentioned SSRF vulnerability to execute arbitrary commands on a vulnerable Exchange Server in the security context of SYSTEM.

CVE-2021-26858 AND CVE-2021-27065
Both of these post-authentication arbitrary files write vulnerabilities allow an authenticated user to write files to any path on a vulnerable Exchange Server. A malicious actor could leverage the previously mentioned SSRF vulnerability to achieve admin access and exploit this vulnerability to write web shells to virtual directories (VDirs) published to the internet by the server’s Internet Information Server (IIS). IIS is Microsoft’s web server, a dependency that is installed with Exchange Server and provides services for Outlook on the web, previously known as Outlook Web Access (OWA), Outlook Anywhere, ActiveSync, Exchange Web Services, Exchange Control Panel (ECP), the Offline Address Book (OAB) and Autodiscover.

Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Global DDOS Attack Campaign Targets Several VOIP Providers

Bandwidth.com has become another victim in a global distributed denial of service(DDOS) attack campaign which is targeting VoIP providers this month. The campaign has to lead to nationwide outages this week. Bandwidth is a voice over Internet Protocol (VoIP) services company that provides voice telephony over the Internet to businesses and resellers.

On September 25th Bandwidth began reporting that they were experiencing unexpected failures with their voice and messaging services.

“Bandwidth is investigating an incident impacting Voice and Messaging Services. Calls and Messages may experience unexpected failures. All teams are actively engaged,” reported Bandwidth on their status page.

Since the DDOS attacks began, Bandwidth has been providing frequent status updates detailing outages affecting voice, Enhanced 911 (E911) services, messaging, and access to the portal.

Bandwidth is a leading telephony provider for US VoIP companies, and due to the DDOS attack, many other VoIP vendors reported outages over the past few days, including Twilio, Accent, DialPad, Phone.com, and RingCentral.

Though it is not confirmed if all these outages are related to the DDOS attack, one outage report directly mentions Bandwidth while the others state that an upstream provider was involved.

“The upstream provider has indicated that service has returned to normal operation. We will continue to monitor this situation and report any new information as it becomes available. Customers should be prepared for potential impairments of inbound services within 12-16 hours as the potential exists for this DDoS attack to return. We will not close this issue until services have returned to the normal operation for a period of 72 hours.” said the report on Accent’s page.

Twilio initially told reporters at BleepingComputer they were not affected by the DDOS attack on Bandwidth, but their status page states that they had issues with Bandwidth on September 27th.

“Monitoring – We are observing recovery in Twilio Voice call quality and connection issues. Bandwidth is reporting the issue resolved as well. We will continue monitoring the service to ensure a full recovery. We will provide another update in 2 hours or as soon as more information becomes available.” said a representative on Twilio’s status page.

Initial DDOS Attacks

Early this month, VoIP provider VoIP.ms suffered a catastrophic week-long DDoS attack that took down almost all of their services and portals, leaving their customers without voice services.

The attack was tied up with extortion, where hackers began impersonating the notorious ransomware group REvil. They initially demanded one bitcoin ($45,000) to halt their attacks but later increased it to 100 bitcoins ($4.5 million).

Due to that DDOS attack, Bandwidth customers immediately suspected that Bandwidth was also suffering from a similar DDoS attack.

Because VoIP services are routed over the internet and require endpoints to be publicly accessible, they are easy pickings for DDOS extortion attacks.

During these attacks, hackers will overwhelm servers, portals, and gateways by sending more requests than can be handled and thus making the targeted devices and servers inaccessible to anyone else.

Bandwidth did not initially make an official statement on the attack, but employees informed customers of the DDOS attacks.

One such customer shared a screenshot on Reddit of a customer support message allegedly from a Technical Assistance Center manager who states that a DDoS attack is responsible for the outages.

“Bandwidth continues to experience a DDoS attack which is intermittently impacting our services. Our network operations and engineering teams continue active mitigation efforts to protect our network,” reads the screenshot.

On Monday night, Bandwidth said that services had been restored; it was not clear had they paid a ransom or not at this time. Attack resumed again Tuesday morning – it is common for threat actors to briefly halt attacks while they push extortion attempts.

Following the restart of the attack, Bandwidth came clean about the nature of the outages, confirming that they were being hit by a DDOS attack. Bandwidth CEO, David Morken, had the following to say:

“Bandwidth and a number of critical communications service providers have been targeted by a rolling DDoS attack. While we have mitigated much intended harm, we know some of you have been significantly impacted by this event. For that I am truly sorry.

You trust us with your mission-critical communications. There is nothing this team takes more seriously. We are working around the clock to support your teams and minimize the impact of this attack. Our account managers and support teams have been actively reaching out to customers individually to address any issues. If you are experiencing problems and you haven’t heard from us yet, please let us know.

Real-time updates will continue to be posted at status.bandwidth.com. We will not rest until we end this incident, and will continue to do all we can to protect against future ones. Thank you for your patience.”

Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Data Breach Compromises 3.1M Neiman Marcus Customer Card Details

Dallas-based Neiman Marcus Group has been hit in a data breach dating back well over a year. The clothing company took 17 months to notice the breach, which affected 3.1M customers. This week, Neiman Marcus acknowledge the data breach, stating that included personal customer information like names, contact information, payment card information (without CVV codes), gift card numbers (without PINs), usernames, passwords, and even security questions associated with online Neiman Marcus accounts.

The group, which also controls the brands Bergdorf Goodman, Neiman Marcus Last Call, and Horchow, said 3.1 million cards were affected in total during the data breach.

“No active Neiman Marcus-branded credit cards were impacted,” the company’s statement said. “At this time, the Company has no evidence that Bergdorf Goodman or Horchow online customer accounts were affected.”

Neiman Marcus is working with law enforcement and cybersecurity company Mandiant to get more information about the retailer’s data breach, the company said.

“At Neiman Marcus Group, customers are our top priority,” Geoffroy van Raemdonck, the company’s CEO, said in the announcement of the data breach. “We are working hard to support our customers and answer questions about their online accounts. We will continue to take actions to enhance our system security and safeguard information.”

It is believed that given the time it took Neiman Marcus to disclose the data breach, many of the cards that were exposed are expired.

While Neiman Marcus is seemingly playing down the data breach, Chris Clements, VP of solutions architecture at Cerberus Sentinel, was blunter.

“The lack of both prevention and detection capabilities at many organizations is simply staggering,” Clements said. “I try as much as possible to shy away from victim blaming, but in many circumstances, organizations have been grossly negligent in securing customer data.”

Clements added that in many breaches, it’s very easy for an attacker to get their hands on customer data.

“Despite the press releases that almost never fail to describe the attackers or attack methods as ‘highly sophisticated,’ the reality is that most breaches aren’t some ‘super cyber heist plot’ out of a bad movie, but rather akin so some guy walking in the front door and wheeling out a file cabinet and no one is around to notice.”

Justin Fier with Darktrace, said that Neiman Marcus’s IT security team should take the position that the hackers involved have been lurking within their system since May 2020 when the initial attack took place. He adds that it’s the responsibility of Neiman Marcus to adopt a more modern security strategy.

“Today, the most cyber mature retailers are relying on artificial intelligence for everything from credit fraud to supply logistics and, of course, to continually monitor their risk across globally distributed networks and complex digital infrastructures”.

“As retailers like Neiman Marcus adapt to a more virtual world and embrace innovations to support remote shopping (like its recently announced virtual sneaker showroom) we should expect attacks on the industry to increase. These innovations open more avenues for attackers to poke to access the private data of consumers. Businesses have a responsibility to ensure their consumers’ personal data is protected with the best defensive technology available to them.” Fier continued.

At the moment, Neiman Marcus is asking customers to reset their passwords and has set up a call center for those concerned about their information being compromised during the data breach.

Nick Sanna, CEO of RiskLens, said retailers are under both ethical and regulatory obligations to protect customer data.

“They have an obligation to keep this sensitive customer data safe and out of the hands of the wrong people, obligations that are both ethical and regulatory in nature,” Sanna said. “The outcome of not doing this is exactly what Neiman Marcus Group is now facing.”

Protection Against Data Breaches

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

JVCKenwood Get Hit With $7 Million Conti Ransomware Attack

JVCKenwood has been infected in a Conti Ransomware attack where the hackers have stolen 1.7TB of data and are demanding a ransom fee of $7 Million.

JVCKenwood is a multinational electronics company based out of Japan that employs 16,956 people and has a 2021 revenue of $2.45 billion. The company is known for its brands JVC, Kenwood, and Victor, which manufacture car and home audio equipment, healthcare and radio equipment, professional and in-vehicle cameras, and portable power stations.

This week, the company disclosed that servers belonging to its sales division in Europe were hacked on September 22nd, and the Conti Ransomware gang accessed and stole data during the incident.

“JVCKENWOOD detected unauthorized access on September 22, 2021 to the servers operated by some of the JVCKENWOOD Group’s sales companies in Europe. It was found that there was a possibility of information leak by the third party who made the unauthorized access,” JVCKENWOOD announced in a press statement.

“Currently, a detailed investigation is being conducted by the specialized agency outside the company in collaboration with the relevant authorities. No customer data leak has been confirmed at this time. The details will be announced on the company website as soon as they become available.”

The ransom note left by Conti Ransomware has been shared by several media sources since.

In the negotiation chat, the Conti Ransomware gang claims to have stolen 1.5 TB of files and is demanding $7 million not to publish the data and provide a file decryptor.

In an attempt to up the credibility of the attack, the gang shared a PDF file indicating it is a scanned passport for a JVCKenwood employee.

It is believed that there has been no further contact from the JVCKenwood representative, possibly indicating the company will not pay the ransomware.

Conti is a ransomware family believed to be operated by the TrickBot threat actor group and is commonly installed after networks are compromised by the TrickBot, BazarBackdoor, and Anchor trojans.

Conti Ransomware has been responsible for a range of attacks, especially in the last 12 months. These include high-profile attacks against the City of Tulsa, Ireland’s Health Service Executive (HSE), Advantech, and numerous health care organizations.

Last week, a joint report between the FBI, CISA, and NSA warned of escalating Conti ransomware attacks.

Conti Ransomware Analysis

Note: The Analysis of Conti Ransomware was carried out by researchers at Vipre Labs.

Conti ransomware encrypts the files of their victims and publishes the data on their website similar to what other strains do. This extortion behavior is visible on their ransom note saying “We’ve downloaded your data and are ready to publish it on our news website”.

When executed, it will start to encrypt files and change the file extension of the encrypted files to .ODMUA. Like other ransomware, it will leave a ransom note that has a filename “readme.txt”.

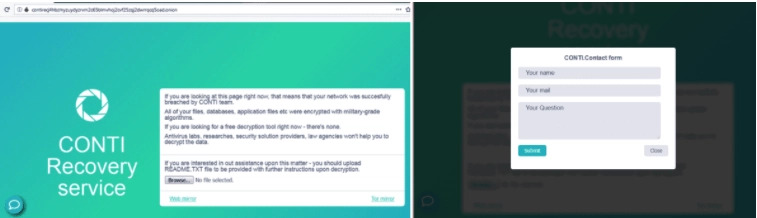
The Conti ransomware website has an instruction on how to upload the README.txt for the decryption and a contact button at the bottom left of the page. Once you click the contact button, a form will appear where you will provide your contact information and question as shown below.

Conti Ransomware Website

Conti ransomware will perform a known malware technique called process hollowing. It is where the malware will create a process in a suspended state, unmaps or removes the PE image layout from a given process space using ZwUnmapViewofSection function, write it’s malicious code using WriteProcessMemory, set a new entry point using SetThreadContext, and resume the execution of the suspended process using the ResumeThread function.

Upon research, we found out that the use of -p argument is to encrypt a specific directory with a single thread and the -m argument is to encrypt the files with multiple threads. It means that Conti ransomware has a multi-threading capability. Multi-threading is where main ransomware creates child threads to speed up the encryption.

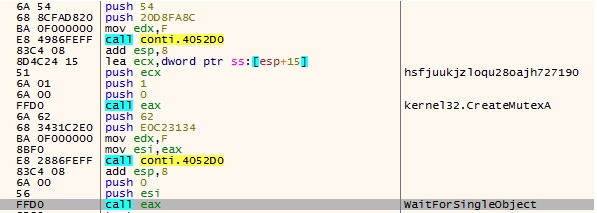
It will use a string “hsfjuukjzloqu28oajh727190” that was decrypted using the decryption of string routine mentioned above for creating a mutex using CreateMutexA function. Then check if there’s an already running mutex. This was commonly used by ransomware to avoid infecting the system more than once.

The Mutex Object
The Mutex Object

It will also delete all the shadow volume copies on the infected system to ensure that the victims won’t be able to recover their encrypted files.

After deleting the shadow copies, Conti ransomware will now start its file encryption by first creating the ransom note which will be first drop in C drive using “CreateFileW” and write the content of its ransom note using “WriteFile”.

As with other ransomware, it will utilize the functions “FindFirstFileW” and “FindNextFileW” to find the files they will encrypt. Conti ransomware has a list of files/file extension and directories which will be excluded for the infection.

When Conti finds the file to be encrypted, it will now generate keys that will be used to encrypt the files. It will used the handle returned by calling the function “CryptAcquireContext” that request a cryptographic context from the Microsoft Enhanced Cryptographic Provider, then the “CryptGenRandom” function to generate cryptographically random bytes, and “CryptEncrypt” function. It leverages AES 256 encryption for their infection.

Then it will open the target file using the “CreateFile” function and retrieve the size of the target file using “GetFileSize”. After this the malware will decrypt different file extensions and check if the file extension of the targeted file is in the list.

Conti ransomware will not just encrypt the files of the infected machine but also spreads and infects the other machine on the same network using SMB protocol.

Protection

Attacks like the Conti Ransomware campaign show that cyberattacks are increasing at an exponential rate, and both government and business leaders are underprepared to face the fallout of an attack. There are several tools internet users should use to increase their online protection. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Chinese VPNs Are Recording World Data On a Massive Scale

AN OVERVIEW OF THE GROWING THREAT

Approximately 20% of the world’s global population are being either directly or potentially set up for the Chinese government to collect all of their private emails, messenger conversations, personal records, as well as the psychological information that could be assessed from that data. The potential harvesting of this VPN data should concern us all.

“Everyone sees what you appear to be, and few experience what you really are.” ― Niccolò Machiavelli, The Prince

CHINA CAN ACCESS 20% OF THE WORLD’S PRIVATE DATA

There are 4.57 billion Internet users in the world.i 31% of those use a VPN.ii Upon reviewing a sample size of 30 popular VPNs, we can estimate that approximately 62% of those are secretly Chinese-owned VPNs currently installed on 878,354,000 consumer user devices.iii Thus, we can estimate with arithmetic the following:

(4,570,000,000 Internet users x 31% VPN users) x 62% Chinese-owned VPNs
= 878,354,000 Chinese-owned VPNs installed on user devices worldwide.

In 2020, 29% of Americans reported using a VPN for personal use (up from 11% in 2019). Of the 275 million Internet users in the US, this means that 39 million Americans may be sharing embarrassing, personal, or otherwise secret data with China. Earlier this year, a number of VPN company databases were breached and leaked; these VPNs claimed to not keep user logs, yet they did. UFO VPN, based out of Hong Kong, is among them. The total amount of log data leaked exceeds one terabyte. In other words, simply because a VPN claims to not have logs does not mean they can be trusted on their word, when the CCP is involved. iv

STATE ACTORS SNOOPING ON AMERICANS IN THE VPN SPACE?

The free world’s vulnerability to shady VPNs is evident in all levels of the industry, including top market share companies. It is very hard to raise capital to start a business. It is very hard to run a business once that capital has been raised. It is almost impossible to raise capital for a business with political goals that run counter to the profit motive. Ergo, when VPN businesses get political, we may consider that smoke indicates a fire, with fire being evidence that the business in question may be a state-supported surreptitious operation designed to collect mass population data. Let’s start with the most obvious facts. VPNs make money pursuing the following markets, with video streaming at the top.

If one were to start a VPN business, the foremost priority would be to maximize profit by focusing on the largest segment of users: video streaming by circumventing geo-blocking. If a VPN were to go against the grain and seek out more fickle, suspicious, and narrowly focused customers, one could argue this is not the best use of capital. When businesses start to move away from focusing on profit, they may raise red flags as supporting state actor initiatives: or aligning with them. Express VPN is one of those curious cases.

Express VPN is a Hong Kong company that is officially registered as a company in the British Virgin Islands. Using Internet Archive, we can see that they used to announce their place of business as Hong Kong.v For more than a decade they obscured their ties to Hong Kong, China, through an offshore shell company in the British Virgin Islands (ie. a shell company that exists only on paper).

In terms of market share, Express VPN ranks in the top 5 in the United States and the world.vi Their daily user number comes close to 5 and 15 million users per day.

The above suggests Express VPN earned 50 million and 150 million dollars per month at an average subscription price of $10 per month. Despite this their BVI companies appears to report less than 0.1038 million in sales while we can estimate real revenue reaching 600 million to 1.2 billion in revenue per year, just not recorded in their offshore company in the BVI that they swear is their headquarters. See “Express VPN Inconsistencies.”vii Let’s look at their recruiter, Nicholas Lui, employee of Network Guard.

It would appear that he has done recruiting for both Network Guard as well as ExpressVPN. Additionally, it appears that both share the same office, as evidenced in our write up about Express VPN. This is where it gets more interesting. If we go to https://chengbao.com.hk/ it redirects us to https://networkguard.com/. (Chengbao is Mandarin for “fortress.”)

  • Employees of Chengbao and Express populate the NG logo; when we click on NG on either profile both go to Network Guard. Network Guard has Express VPN Employees all over their activities. They also share stock photos from the same office.
  • Chengbao Ltd may be the de facto operating company for Express VPN, and Express VPN is a worthless British Virgin Islands shell company reducing, their fair share of taxes with their earnings reporting not reflecting the scale of their business making up a broad segment of the international VPN market share.