Gafgyt Botnet Absorbs Code From Notorious Mirai Strain

The Gafgyt botnet, known for attacks using IoT devices, has absorbed code from the Mirai botnet. The latter also focuses on using IoT devices in its arsenal and released its code publicly several years ago. Researchers have discovered updated variants of Gafgyt using several functions ripped straight from Mirai, allowing Gafgyt to compromise Huawei, Realtek, and Dasan GPON devices. The botnet was already known to target devices from ASUS and other large IoT manufacturers. It also often uses known vulnerabilities such as CVE-2017-17215 and CVE-2018-10561 to download next-stage payloads to infected devices.

The latest variants have now incorporated several Mirai-based modules, according to research from Uptycs released last Thursday, along with new exploits. Variants of Mirai, and indeed other botnets re-using Mirai modules have become more common since the developers released the code base in 2016.

The capabilities taken from Mirai including different methods to carry out DDOS attacks:

HTTP flooding is a kind of DDoS attack in which the attacker sends a large number of HTTP requests to the targeted server to overwhelm it. The creators of Gafgyt have re-used this code from the leaked Mirai source code. 

Comparison between Gafgyt and Mirai’s HTTP Flooding Module

UDP flooding is a type of DDoS attack in which an attacker sends several UDP packets to the victim server as a means of exhausting it. Gafgyt contained this same functionality of UDP flooding, copied from the leaked Mirai source code.

Comparison between Gafgyt and Mirai’s UDP Flooding Module

TCP flood module – Gafgyt performs all types of TCP flood attacks like SYN, PSH, FIN, etc. In this type of attack, the attacker exploits a normal three-way TCP handshake the victim server receives a heavy number of requests, resulting in the server becoming unresponsive. The below image shows the TCP flooder module of Gafgyt, which contained the similar code from Mirai

 
Comparison between Gafgyt and Mirai’s TCP Flooding Module

STD module – Gafgyt contains an STD module which sends a random string (from a hardcoded array of strings) to a particular IP address. This functionality has also been used by Mirai.
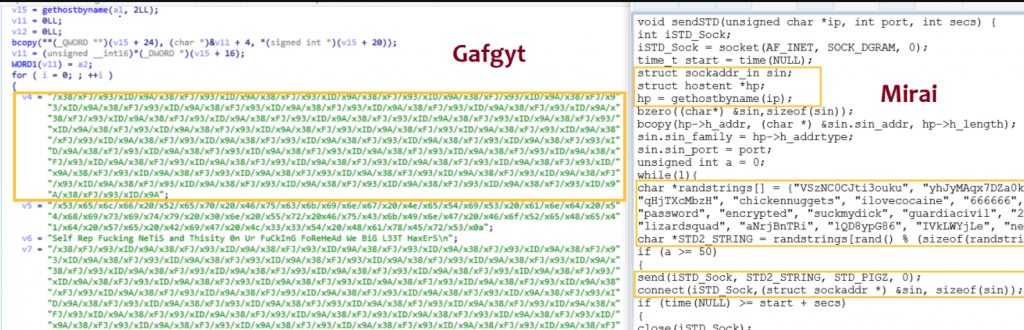
 
Comparison between Gafgyt and Mirai’s STD Flooding Module

Brute force module – Not only are flooding modules are being used. Recent Gafgyt also contained other modules with little tweaks, like a telnet bruteforce scanner

 
Comparison between Gafgyt and Mirai’s telnet bruteforce scanner

Meanwhile, the latest versions of Gafgyt contain new approaches for achieving initial compromise of IoT devices, Uptycs found; this is the first step in turning infected devices into bots to later perform DDoS attacks on specifically targeted IP addresses. These include a Mirai-copied module for Telnet brute-forcing, and additional exploits for existing vulnerabilities in Huawei, Realtek and GPON devices.

Gafgyt botnet uses the Huawei exploit (CVE-2017-17215) and the Realtek (CVE-2014-8361) exploit for remote code execution (RCE), which is used to fetch the Gafgyt payload.

“The Gafgyt malware binary embeds RCE exploits for Huawei and Realtek routers, by which the malware binary, using ‘wget’ command, fetches the payload,” according to Uptycs. “[It] gives the execution permission to payload using ‘chmod’ command, [and] executes the payload.”

The GPON exploit (CVE-2018-10561) is used for authentication bypass in vulnerable Dasan GPON routers; here, the malware binary follows the same process, but can also remove the payload on command.

“The IP addresses used for fetching the payloads were generally the open directories where malicious payloads for different architectures were hosted by the attacker,” researchers added.

Before Gafgyt Botnet: The Storied History of Mirai

The Mirai Botnet has been around for several years. While other malware may go into periods of slow activity, Mirai has remained at the forefront of botnet headlines since its inception.

Perhaps Mirai’s most infamous attack came on October 12, 2016. On that date, a massive denial of service (DDoS) attack left much of the internet inaccessible on the U.S. east coast. The attack, which authorities initially feared was the work of a hostile nation-state, was in fact the work of the Mirai botnet.

This attack, which initially had much less grand ambitions grew more powerful than its creators ever dreamed possible. The origins of the botnet were speculated for some time, many believing it to be the work of high-profile cybercriminals. Instead, Mirai was created by a group of three friends who were using the botnet to run an extortion ring on Minecraft servers, a video game they played together.

It encapsulated some clever techniques, including the list of hardcoded passwords. But, in the words of an FBI agent who investigated the attacks, “These kids are super smart, but they didn’t do anything high level—they just had a good idea.”

Much more damaging than simply developing the botnet, the creators released the source code publicly in 2016. This has lead to a wild fire of Mira-related attacks, and researchers estimate there are more than 60 variations of the botnet currently.

Mirai has a few key characteristics seen across all variations of it:

  • Mirai can launch both HTTP flood and network-level attacks
  • There are certain IP address ranges that Mirai is hard-wired to avoid, including those owned by GE, Hewlett-Packard, and the U.S. Department of Defense
  • Upon infecting a device, Mirai looks for other malware on that device and wipes it out, in order to claim the gadget as its own
  • Mirai’s code contains a few Russian-language strings. This was intended to be a red-herring on its origin, but still remains in variations

Protection

With evolving botnet tools like Gafgyt posing new threats every day, its important you use the tools required to protect your devices. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.
Ryuk Ransomware Gets Updated Attack Vector Options

Recent attacks from the gang behind the Ryuk Ransomware have shown that the notorious virus has been updated to contain a new attack vector when it comes to gaining initial access to a victim’s network. According to BleepingComputer, “The trend observed in attacks this year reveals a predilection towards targeting hosts with remote desktop connections exposed on the public internet.”. The Ryuk gang do still seem to favor their initial attack vector, however – phishing emails.

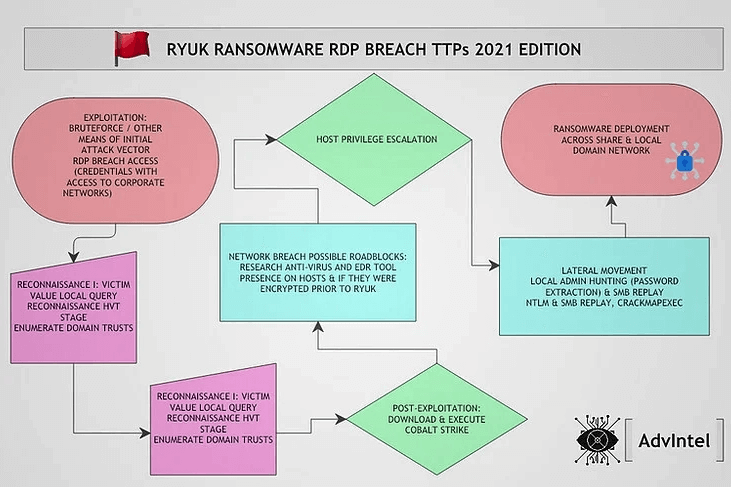
Security researchers from the threat intelligence boutique Advanced Intelligence (AdvIntel) observed that Ryuk ransomware attacks this year relied more often on compromising exposed RDP connections to gain an initial foothold on a target network.

The actors have been running “large-scale brute force and password spraying attacks against exposed RDP hosts” to compromise user credentials.

Another attack vector used by the gang recently has been the spear-phishing BazarCall campaign. This campaign saw the attackers distribute malware through malicious call centers that targeted corporate users and directed them to weaponized Excel documents. SaferNet covered that campaign in a recent post.

AdvIntel noted that attacks this year in 2021 have relied more on scanning for exposed RDP hosts, rather than phishing.

Researchers stated that the Ryuk gang undertook reconnaissance in two stages. One was to determine what kind of valuable resources are on the compromised domain. The second stage is to find information about the company’s finances, in order to set an appropriate ransom fee for the ransomware.

While searching the active directory, Ryuk Ransomware uses Adfind, an AD query tool, and the post-exploitation tool Bloodhound that explores relationships in an Active Directory domain to find attack paths.

Ryuk Ransomware RDP Breach Courtesy of AdvIntel

Getting financial details about the victim relies on open-source data. AdvIntel says that the actors search on services like ZoomInfo for information about the company’s recent mergers and acquisitions and other details that can increase the profitability of the attack.

Additional reconnaissance is carried out using the Cobalt Strike post-exploitation tool that’s become a standard in most ransomware operations and scans that reveal the security products like antivirus and endpoint detection response (EDR) defending the network.

Among other new attacks used by the Ryuk Ransomware gang was the use of KeeThief, an open-source tool for extracting credentials from KeePass password manager.

KeeThief works by extracting key material (e.g. master password, key file) from the memory of a running KeePass process with an unlocked database.

Vitali Kremez, the CEO of AdvIntel, told BleepingComputer that the attackers used KeeThief to bypass EDR and other defenses by stealing the credentials of a local IT administrator with access to EDR software.

Another tactic was to deploy a portable version of Notepad++ to run PowerShell scripts on systems with PowerShell execution restriction, Kremez says.

According to researchers, Ryuk Ransomware attacks in 2021 are making use of exploits on two vulnerabilities, both of which can be patched out. These are:

CVE-2018-8453 – high-severity (7.8/10) privilege escalation in Windows 7 through 10 and Windows Server 2008 through 2016 that allows running an arbitrary kernel with read/write permissions because the Win32k component fails to properly handle objects in memory.

CVE-2019-1069 – high-severity (7.8/10) privilege escalation in Windows 10, Windows Server 2016, and 2019 because of the way the Task Scheduler Service validates certain file operations, which enables a hard link attack.

“Once actors have successfully compromised a local or domain admin account, they distribute the Ryuk payload through Group Policy Objects, PsExec sessions from a domain controller, or by utilizing a startup item in the SYSVOL share”, AdvIntel said.

According to the company, organisations should take the following mitigation steps:

  • Detect the use of Mimikatz and the execution of PsExec on the network
  • Alerts for the presence of AdFind, Bloodhound, and LaZagne on the network
  • Ensure that operating systems and software have the latest security patches
  • Implement multi-factor authentication for RDP access
  • Network segmentation and controls to check SMB and NTLM traffic
  • Use the principle of least privilege and routine checks for account permissions
  • Routine review of Routinely review account permissions to prevent privilege creep and maintain the principle of least privilege
  • Routinely review of Group Policy Objects and logon scripts
  • Patch systems against CVE-2018-8453 and CVE-2019-1069

Ryuk Ransomware is the most notorious Ransomware client on the web today, and has collected over $150 million in ransom demands. Changing up tactics is just a sign of an ever-evolving threat.

Protection

When cyberthreats grow every day, it’s important business owners use updated tools to combat the dangers their businesses face. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

BazarLoader Malware Targets Slack and Basecamp

The BazarLoader Malware is engaging in a campaign that targets users of work collaboration tools Slack and Basecamp. The attack utilizes email messages with links to malware payloads. Slack is a popular tool used for communication amongst teams, particularly those who work remotely. Basecamp focuses on project management but also allows for team communication. Similar to Slack, Basecamp is popular amongst remote workers. Both tools are used even in office environments.

We have reported at length on BazarLoader at SaferNet, most recently last week, when the malware was being distributed as a part of the BazarCall campaign. This campaign took a novel route by using call centers for social engineering.

The purpose of BazarLoader Malware is effectively to act as a Malware Loader. BazarLoader tends to distribute TrickBotIcedIDGozi IFSB, and other malware. Notably, it has also been distributing the notorious Ryuk Ransomware. These infections are hazardous as they provide remote access to compromised corporate networks where the threat actors spread laterally through the network to steal data or deploy ransomware.

“With a focus on targets in large enterprises, BazarLoader could potentially be used to mount a subsequent ransomware attack,” according to an advisory from Sophos, issued on Thursday.

According to researchers at Sophos, in the first campaign spotted, adversaries are targeting employees of large organizations with emails that purport to offer important information related to contracts, customer service, invoices or payroll.

“One spam sample even attempted to disguise itself as a notification that the employee had been laid off from their job,” according to Sophos.

The links in the malicious emails are hosted on Slack or Basecamp. This means that if the target uses either service, the link could appear legitimate. Given how popular these platforms and remote working have grown, this is likely.

“The attackers prominently displayed the URL pointing to one of these well-known legitimate websites in the body of the document, lending it a veneer of credibility,” researchers said. “The URL might then be further obfuscated through the use of a URL shortening service, to make it less obvious the link points to a file with an .EXE extension.”

If the victim clicks on the link, the BazarLoader malware downloads on the machine and is installed. These executable files, when run, inject a DLL payload into a legitimate process, such as the Windows command shell, cmd[.][exe].

“The malware, only running in memory, cannot be detected by an endpoint protection tool’s scans of the filesystem, as it never gets written to the filesystem,” explained researchers. “The files themselves don’t even use a legitimate .DLL file suffix because Windows doesn’t seem to care that they have one; The OS runs the files regardless.”

It is believed that BazarLoader is connected to Trickbot, in that the creators of each are possibly one and the same. TrickBot is another first-stage loader malware often used in ransomware campaigns.

Sophos looked into the connection and found that the two malwares use some of the same infrastructure for command and control.

“From what we could tell, the [BazarLoader] malware binaries running in the lab network bear no resemblance to TrickBot,” according to the posting. “But they did communicate with an IP address that has been used in common, historically, by both malware families. Of course, a lot of people have studied this connection in the past.”

In any event, BazarLoader appears to be in an early stage of development and isn’t as sophisticated as more mature families like TrickBot, researchers added.

For instance, “while early versions of the malware were not obfuscated, more recent samples appear to encrypt the strings that might reveal the malware’s intended use,” they said.

BazarLoader Malware Analysis

BazarLoader has been analysed in depth by cybersecurity researchers at AT&T Cybersecurity department.

The BazarLoader authors have produced an advanced module, with a significant amount of obfuscation. The BazarLoader uses multiple routines to hide API calls and embedded strings, which are then decrypted and resolved at runtime.

Once executed, the loader will allocate memory to store and decrypt its shellcode, which will be allocated to a NUMA node for faster execution. After allocation and decryption, the next instructions will jump to the shellcode that will be executed on the heap.

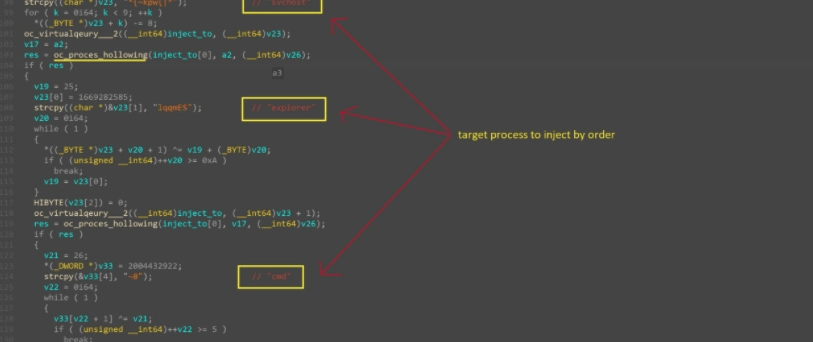
Next, the malware will try to communicate with .bazar domain C2 servers. Once the C2 has been established, the loader will try to inject its payload into a system process using the process hollowing technique (T1093), which will create a suspended thread, unmap the destination image from memory, allocate new memory in the target process, copy the shellcode into the target process, set the thread context, and resume the process.

The loader will first attempt to inject into an “svchost” process, and if injection fails, it will try to inject into the “explorer[.][exe]” process, and if injection fails again as a last-ditch effort the loader will attempt to inject into the “cmd[.][exe]” process. For persistence the loader will create a registry key under “HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Winlogon\Userinit”.

The malware uses the Windows API “VirtualAllocExNuma” function to allocate memory for its shellcode to be executed. The “VirtualAllocExNuma” function is used to allocate memory on a NUMA node, which allows for faster execution. The implementation can be seen In Figure 1 below. It is interesting to note that the “VirtualAllocExNuma” function is not commonly used in process injection.

API Resolution and Shellcode Decryption Routines

The BazarLoader authors have created dozens of decryption routines, and with almost each string including APIs, DLLs, and C2s there is a once per use unique decryption routine. The loader uses the same decryption technique described above to resolve the API calls it uses during execution.

For injection, the malware resolves APIs from the ntdll.dll after it loads from disk and checks that there are no inline hooks within its function, that could be created for example by AV software that tracks those API calls.

The load order of APIs called in the injection procedure is:

  • CreateProcessA (CREATE_SUSPENDED | CREATE_NEW_CONSOLE)
  • NtGetContextThread
  • NtReadVirtualMemory
  • NtUnmapViewOfSection
  • VirtualAllocExA
  • NtWriteVirtualMemory
  • NtSetContextThread
  • NtResumeThread

The obfuscated C2 servers are decrypted in the function shown below:

C2 Domains forgame[.]bazar and bestgame[.]bazar

Protection

Education is also the key to defense against attacks like these. Outwitting social engineering attempts is the only guaranteed way not to fall victim to campaigns like BazarLoader. For times when a dupe may be unclear, it’s important to have the tools necessary to back you up. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.
NSA Warns Of 5 Security Exploits Being Used By Russia

United States government security agencies, including the NSA, have released a joint advisory warning citizens of the most threatening security exploits being used by the Russian Foreign Intelligence Service (SVR). The SVR’s cyber department has previously been nicknamed Cozy BearAPT29, and The Dukes by various cybersecurity researchers who have tracked them over the years. Unsurprisingly, Cozy Bear is associated with a staggering amount of cyberattacks in the last five years – Most notably, the SolarWinds attack last year, which the US officially pinned on the group this month.

In the report, the agency outline that SVR/Cozy Bear, “frequently use publicly known vulnerabilities to conduct widespread scanning and exploitation against vulnerable systems in an effort to obtain authentication credentials to allow further access. This targeting and exploitation encompasses U.S. and allied networks, including national security and government-related systems.”

As well as SolarWinds, SVR/Cozy Bear has been behind a number of attacks in the last 12 months. These include targeting COVID-19 research facilities through deploying WellMess malware and leveraging a VMware vulnerability that was a zero-day at the time for follow-on Security Assertion Markup Language (SAML) authentication abuse. SVR cyber actors also used authentication abuse tactics following SolarWinds-based breaches.

The SVR/Cozy Bear has exploited — and continues to successfully exploit —software vulnerabilities to gain initial footholds into victim devices and networks. Outlined in the report, the 5 most notable exploits are as follows:

CVE-2018-13379 – This exploit concerns Fortinet. In Fortinet Secure Sockets Layer (SSL) Virtual Private Network (VPN) web portals, an ImproperLimitation of a Pathname to a Restricted Directory (“Path Traversal”) allows an unauthenticated attacker to download system files via special crafted HTTP resource requests. Threat actors have extensively used this vulnerability in the past to target government agencies and corporate networks, including U.S. govt elections support systems, COVID-19 research organizations, and more recently, to deploy the Cring ransomware.In November 2020, a threat actor leaked the credentials for almost 50,000 Fortinet VPN devices on a hacker forum.

CVE-2019-9670 – An exploit affecting Synacor Zimbra Collaboration Suite, the mailboxd component has an XML External Entity injection (XXE) vulnerability.

CVE-2019-11510 – In Pulse Secure VPNs, an unauthenticated remote attacker can send a specially crafted Uniform Resource Identifier (URI) to perform an arbitrary file read. Pulse Secure VPNs have been a favorite for threat actors for some time, being used to gain access to US government networks, attack hospitals, and deploy ransomware on networks.

CVE-2019-19781 – Citrix Application Delivery Controller (ADC) and Gateway allow directory traversal. The CVE-2019-19781 exploit is known to be used by threat actors, including ransomware gangs, to gain access to corporate networks and deploy malware.

CVE-2020-4006 – VMware Workspace One Access, Access Connector, Identity Manager, and Identity Manager Connector have a command injection vulnerability. In December 2020, the US government warned that Russian state-sponsored threat actors were exploiting this vulnerability to deploy web shells on vulnerable servers and exfiltrate data.

The report has given several mitigation steps for system owners:

NSA, CISA, and FBI recommend that critical system owners prioritize the following mitigation actions to mitigate the loss of sensitive information that could impact U.S. policies, strategies, plans, ongoing operations, and competitive advantage. Additionally, due to the various systems and networks that could be impacted outside of these sectors, NSA, CISA, and FBI recommend that the following mitigations be prioritized for action by all network defenders.

While some vulnerabilities have specific additional mitigations below, the following general mitigations apply:

  • Keep systems and products updated and patch as soon as possible after patches are released since many actors exploit numerous vulnerabilities.
  • Expect that the risk from data stolen or modified (including credentials, accounts, and software) before a device was patched will not be alleviated by patching or simple remediation actions. Assume that a breach will happen, enforce least-privileged access, and make password changes and account reviews a regular practice.
  • Disable external management capabilities and set up an out-of-band management network.
  • Block obsolete or unused protocols at the network edge and disable them in device configurations.
  • Isolate Internet-facing services in a network Demilitarized Zone (DMZ) to reduce exposure of the internal network.
  • Enable robust logging of Internet-facing services and authentication functions. Continuously hunt for signs of compromise or credential misuse, particularly within cloud environments.
  • Adopt a mindset that compromise happens: prepare for incident response activities, only communicate about breaches on out-of-band channels, and take care to uncover a breach’s full scope before remediating.

As the SVR/Cozy Bear has been utilizing a combination of these exploits in their attacks, it is strongly advised that all administrators install the associated security updates immediately.

The NSA warned last year that two of these exploits, CVE-2019-11510 and CVE-2019-19781, are also in the top 25 vulnerabilities utilized by China state-sponsored hackers.

History of the Group Abusing The Exploits: SVR/Cozy Bear

There is not a widely agreed upon date of Cozy Bear’s first appearance. Researchers have found traces in one of their malware strains, MiniDuke, that points to being active since 2008. Other sources note Cozy Bear first came to fame when hacking minor diplomatic entities in 2010.

As well as MiniDuke, Cozy Bear gained notoriety, developing several other Malware strains in the early 2010s. These include CozyDukeCosmicdukeOnionDukeHAMMERTOSSPolyglotDukeRegDukeFatDuke, and Seaduke.

Cozy Bear is known to program their Malware in assembly language. Assembly is the lowest programming language used, highlighting the groups’ skills. Furthermore, Assembly is the fastest language due to its implied closeness to the hardware; this gives their malware strains lightning-fast processing times.

In March 2014, a Washington, D.C.-based private research institute was found to have Cozyduke (Trojan.Cozer) on their network. Cozy Bear then started an email campaign attempting to lure victims into clicking on a flash video of office monkeys that would also include malicious executables. By July the group had compromised government networks and directed Cozyduke-infected systems to install Miniduke onto a compromised network.

In the summer of 2014, digital agents of the Dutch General Intelligence and Security Service infiltrated Cozy Bear. They found that these Russian hackers were targeting the US Democratic Party, State Department and White House. Their evidence influenced the FBI’s decision to open an investigation.

In August 2015 Cozy Bear was linked to a spear-phishing cyber-attack against the Pentagon email system causing the shut down of the entire Joint Staff unclassified email system and Internet access during the investigation.

In June 2016, Cozy Bear was implicated alongside the hacker group Fancy Bear in the Democratic National Committee cyber attacks. While the two groups were both present in the Democratic National Committee’s servers at the same time, they appeared to be unaware of the other, each independently stealing the same passwords and otherwise duplicating their efforts. A CrowdStrike forensic team determined that while Cozy Bear had been on the DNC’s network for over a year, Fancy Bear had only been there a few weeks. Cozy Bear’s more sophisticated tradecraft and interest in traditional long-term espionage suggest that the group originates from a separate Russian intelligence agency.

On February 3, 2017, the Norwegian Police Security Service (PST) reported that attempts had been made to spearphish the email accounts of nine individuals in the Ministry of Defence, Ministry of Foreign Affairs, and the Labour Party. The acts were attributed to Cozy Bear, whose targets included the Norwegian Radiation Protection Authority, PST section chief Arne Christian Haugstøyl, and an unnamed colleague. Prime Minister Erna Solberg called the acts “a serious attack on our democratic institutions.”

In February 2017, it was revealed that Cozy Bear and Fancy Bear had made several attempts to hack into Dutch ministries, including the Ministry of General Affairs, over the previous six months. Rob Bertholee, head of the AIVD, said on EenVandaag that the hackers were Russian and had tried to gain access to secret government documents.

Suspicions that Cozy Bear had ceased operations were dispelled in 2019 by the discovery of three new malware families attributed to Cozy Bear: PolyglotDuke, RegDuke and FatDuke. This shows that Cozy Bear did not cease operations, but rather had developed new tools that were harder to detect. Target compromises using these newly uncovered packages are collectively referred to as Operation Ghost.

And most recently, Cozy Bear was found to be behind the 2020 SolarWinds attack, a supply-chain attacked that crippled large parts of the US. Given their history, and the number of critical exploits the internet is faced with now, it’s unlikely this will be last we’ll hear of the group.

Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

New Saint Bot Malware Downloader Proliferates Via Phishing Emails

Anew malware has surfaced in the wild, dubbed Saint Bot. The Saint Bot Malware is deployed via phishing emails and aims to deploy credential stealers and download other malware strains onto target devices. Saint Bot was first spotted in January 2021; however, a surge of reports of infections along with the strain showing new features points to the idea that Saint Bot is under active development and may very well prove to be a major threat in the coming months.

According to cybersecurity researchers at MalwareBytes, Saint Bot has been gaining slow momentum in the cybercrime world. Researchers noted the malware dropping stealers such as Taurus Stealer and other loaders. It has been designed so that it is a suitable launching point for just about any malware strain.

“Saint Bot employs a wide variety of techniques which, although not novel, indicate some level of sophistication considering its relatively new appearance.” researchers said.

The infection chain analyzed by the MalwareBytes begins with a phishing email containing an embedded ZIP file (“bitcoin.zip”) that claims to be a bitcoin wallet when, in fact, it’s a PowerShell script under the guise of .LNK shortcut file. This PowerShell script then downloads the next stage malware, a WindowsUpdate.exe executable, which, in turn, drops a second executable (InstallUtil.exe) that takes care of downloading two more executables named def.exe and putty.exe.

The payloads for Saint Bot, interestingly, are hosted on Discord. This tactic is becoming popular for hackers, who abuse the functionality of legitimate services for Command-&-Control (C&C) communications, security evasion, and to deploy Malware.

“When files are uploaded and stored within the Discord CDN, they can be accessed using the hardcoded CDN URL by any system, regardless of whether Discord has been installed, simply by browsing to the CDN URL where the content is hosted,” researchers from Cisco Talos disclosed in an analysis earlier this week, thus turning software like Discord and Slack into lucrative targets for hosting malicious content.

“Saint Bot is yet another tiny downloader,” researchers said. “It is not as mature as SmokeLoader, but it is quite new and currently actively developed. The author seems to have some knowledge of malware design, which is visible by the wide range of techniques used. Yet, all the deployed techniques are well-known and pretty standard, [and] not showing much creativity so far.”

Saint Bot Malware Analysis

The bulk of this analysis was carried out by researchers at MalwareBytes, notably by Aleksandra “Hasherezade” Doniec.

As mentioned previously in this article, the first step of the attack is via a phishing email purporting to be a bitcoin wallet. The wallet is a decoy, and instead was in fact an obfuscated PowerShell script that would infect the host with Saint Bot. While the majority of cases have used the bitcoin wallet set-up, Hasherezade noted that the same attack targeted government institutions in Georgia recently, acting as a COVID-themed campaign.

Saint Bot Delivery Roadmap, by MalwareBytes

One the script is run, the main sample drops another executable in the %TEMP% directory. This then downloads two executables named: def.exe, and putty.exe. It saves them in %TEMP% , and tries to execute them with elevated privileges. If run, the first sample (def.exe) deploys a batch script disabling Windows Defender. The second sample (named putty.exe) is the main malicious component.

The scripts from the “AppData/Local/z_[user]” are used to deploy the main sample. During the first run, the executable injects itself into “EhStorAurhn.exe“. Below we can see the injected implant detected and dropped by HollowsHunter.

Inject Implant from Malware Antibytes

Once the implant was injected, it connects to its Command-and-Control server (C&C) and proceeds with its main actions. Observing the network traffic we will find the URL of the malware’s C&C queried repeatedly:

http[:]//update-0019992[.]ru/testcp1/gate.php

Following this URL we can see the related C&C panel, which looks typical for the Saint Bot:

Inject Implant from Malware Antibytes

From here, the hackers are able to trigger commands from the C&C, including downloader further malware strains.

Researchers noted the evolution of the code between the current sample and a sample from January. While January’s contains the same C&C, the code is rewritten. It used a mutex “saint2021_NewGeneration” suggesting that this bot went through some major changes since the beginning of this year.

Protection

The Saint Bot Malware is just another example of new malware strains infecting machines globally. Furthermore, it highlights the issue with phishing – The phishing attack vector is still key to a hackers success, and the weakest link in business cybersecurity.

It is important that business leaders use proactive phishing protection tools to sure their businesses aren’t affected by malware attacks. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

SolarMarker RAT Pushed On 100,000 Google Sites

The SolarMarker RAT is making its way around many websites due to some clever manipulation of Google’s SEO ratings. The attack starts with the potential victim performing a search for business forms such as invoices, questionnaires, and receipts. The attack campaign lays traps for potential victims using Google search redirection and drive-by-download. When a person visits one of the sites they are directed to, the infected site executes a binary disguised as a PDF by clicking on a purported “form.” This will inject the SolarMarker RAT onto their device.

Once the RAT is on the victim’s computer and activated, the threat actors can send commands and upload additional malware to the infected system, such as ransomware, a credential stealer, a banking trojan, or simply use the RAT as a foothold into the victim’s network.

Initial reports and analysis of SolarMarker’s activity came from eSentire earlier this week.

“This is an increasingly common trend with malware delivery, which speaks to the improved security of applications such as browsers that handle vulnerable code,” researchers wrote. “Unfortunately, it reveals a glaring blind spot in controls, which allows users to execute untrusted binaries or script files at will.”

Given how difficult it is to master Google’s SEO for many businesses, it is clear that the hackers behind the SolarMarker RAT attacks are using high levels of sophistication in their campaign.

The hackers use common business words as keywords, which dupes Google’s web crawler into believing that the intended content meets conditions for a high page-rank score, which means the malicious sites will appear at the top of user searches, according to the report. This increases the likelihood that victims will be lured to infected sites.

eSentire’s Threat Response Unit (TRU) discovered over 100,000 unique web pages that contain popular business terms/particular keywords: template, invoice, receipt, questionnaire, and resume. In a precursory search, 70,000 unique web pages included the mention of either template or invoice.

“Security leaders and their teams need to know that the threat group behind SolarMarker has gone to a lot of effort to compromise business professionals, spreading a wide net and using many tactics to successfully disguise their traps,” said Spence Hutchinson, manager of threat intelligence for eSentire.

“Once a RAT has been installed on a victim’s computer, the threat actors can upload additional malware to the device, such as a banking trojan, which could be used to hijack the online banking credentials of the organization,” researchers said. Threat actors also could install a credential-stealer in this way, to harvest the employee’s email credentials and launch a business email compromise (BEC) scheme.

“Unfortunately, once a RAT is comfortably installed, the potential fraud activities are numerous,” they noted.

SolarMarker RAT Analysis

This analysis has been provided be eSentire, who have been researching the SolarMarker RAT attacks.

The emerging RAT is written with the .NET software framework, and tracked as Jupyter, Yellow Cockatoo, SolarMarker, and now being tracked as Polazert on twitter. SolarMarker was first observed in early October 2020. Throughout October and November 2020, SolarMarker utilized docx2rtf.exe as a decoy to distract users as the .NET silently installed itself in the background. Red Canary reports SolarMarker changing this decoy application throughout the following months using in September 2020 photodesigner7_x86-64.exe and Expert_PDF.exe in November 2020, while the eSentire continued to see docx2rtf.exe. Researchers have now discovered that the SolarMarker group is using Slim PDF Reader.

The attack chain starts with a google search and ends in the installation of SolarMarker RAT and lesser-known PDF viewer.
Process tree outlining the installation of SolarMarker. Note the Adobe icon on the installer file. The RAT, labeled (unknown), then goes on to install the decoy document and make malicious PowerShell calls.

SolarMarker RAT captures victims via Google Search redirect. Often, clients are looking for a free version or template of a document. In the latest incident observed by researchers, the victim, who works in the financial industry, was redirected to a Google Sites page controlled by the threat actor with an embedded download button. The download button, hosted at passiondiamond[.]site, is easy to customize. Researchers were able to generate a document named “this is a test” for download.

The Download button that is embedded in the Google Site

The decoy program, Slim PDF, serves as an important visual cue for potential victims of SolarMarker but also helps to lower suspicion of malicious intent.

Screenshot from the Slim PDF reader website

The redirection infrastructure passes through a series of .tk TLDs before landing on the final .ml TLD domain. Upon visiting the infrastructure with a VM, no such redirects are experienced. Upon inspecting the source code of the embedded download button at passiondiamond.site, researchers found an entirely different .tk domain, indicating a possibility that these redirect pathways are dynamic and can be changed for either operational security or delivery efficacy. It’s possible that any number of checks are being performed on the visiting browser and operating system to ensure they are being operated by victims, not security researchers.

SolarMarker’s redirect path from the search result to the final payload site

Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Millions of IoT Devices at Risk From NAME:WRECK Exploits

Exploits are looming over 100 million IoT devices under threat from 9 newly discovered DNS vulnerabilities, discovered by Forescout Research Labs and JSOF and collectively dubbed NAME:WRECK. The NAME:WRECK exploits affect four well-known TCP/IP stacks, each present in popular IT software and IoT firmware. The exploits impact organizations in multiple sectors, from government to healthcare, manufacturing, and retail, and if successfully exploited by malicious actors in a denial of service (DoS) or remote code execution (RCE) attack, could be used to disrupt or take control of victim networks.

The exploits affect the following four stacks:

FreeBSD: Commonly used in computers, printers, and networking devices found on Device Cloud. It is used on other well-known open source projects such as firewalls and some commercial network appliances.

IPNet: Integrator solution offered by IPNet Solutions, geared for enterprise and telecom markets.

NetX: Common product categories include mobile phones, consumer electronics, and business automation, in devices such as printers, smart clocks, systems-on-a-chip, and energy & power equipment in Industrial Control Systems (ICS).

Nucleus NET: Part of Nucleus RTOS, and deployed in over 3 billion devices. Commonly used in building automation, operational technology, and VoIP, as well as ultrasound machines, storage systems, and critical systems for avionics.

The combination of widespread use of these stacks, together with external exposure of the vulnerable DNS clients, results in a dramatically increased attack surface. Even the most conservative estimates conclude that millions of devices are impacted by NAME:WRECK.

“NAME:WRECK is a significant and widespread set of exploits with the potential for large-scale disruption,” said Daniel dos Santos, research manager at Forescout Research Labs. “Complete protection against NAME:WRECK requires patching devices running the vulnerable versions of the IP stacks and so we encourage all organisations to make sure they have the most up-to-date patches for any devices running across these affected IP stacks.

“Unless urgent action is taken to adequately protect networks and the devices connected to them, it could be just a matter of time until these vulnerabilities are exploited, potentially resulting in major government data hacks, manufacturer disruption or hotel guest safety and security.”

Although FreeBSD, Nucleus NET and NetX have all been patched recently, as with many other exploits affecting deployed IoT devices, NAME:WRECK will inevitably be hard to patch in some instances because nowadays, IoT technology is often deeply embedded in organisational systems, can be hard to manage, and often essentially impossible to patch.

Due to the severity of the exploits, Forescout and JSOF are recommending a series of mitigations:

  • Users should try to discover and inventory devices running the vulnerable stacks – Forescout has pushed out an open source script that uses active fingerprinting to do this, which is being updated as new developments occur.
  • Users should enforce segmentation controls and increase network hygiene, restricting external communication paths and isolating vulnerable devices if they cannot be patched.
  • Users should monitor for patches being dropped by affected device suppliers and devise a remediation plan for affected inventory.
  • Users should configure affected devices to run on internal DNS servers, and monitor external DNS traffic (successful exploitation would need a malicious DNS server to reply with malicious packets).
  • Users should monitor all their network traffic for malicious packets trying to exploit known vulnerabilities or zero-days affecting DNS, mDNS and DHCP clients.

NAME:WRECK is the second major set of TCP/IP exploits uncovered by Forescout’s team in the past year as part of a research programme called Project Memoria.

In December 2020, the firm issued a warning over 33 different exploits, referred to as Amnesia33, affecting devices made by over 150 different tech manufacturers. Such was the scale of the Amnesia33 disclosure that it prompted an emergency alert from the US Cyber Security and Infrastructure Security Agency.

NAME:WRECK Exploits Analysis

Much of this analysis has been carried out by Forescout, JSOF, and BleepingComputer.

The researchers analyzing the DNS implementations in the above-mentioned TCP/IP stacks looked at the message compression feature of the protocol. It is not uncommon for DNS response packets to include the same domain name or a part of it more than once, so a compression mechanism exists to reduce the size of DNS messages. Not just DNS resolvers benefit from this encoding as it is present in multicast DNS (mDNS), DHCP clients, and IPv6 router advertisements.

Forescout explains in the report that the feature is also present in many implementations, although some protocols do not officially support compression. This occurs “because of code reuse or a specific understanding of the specifications.”

The researchers note that implementing the compression mechanism has been a tall order, as highlighted by more than a dozen exploits discovered since the year 2000.

Below is a list of the 9 exploits across the four TCP/IP stacks:

CVE-2020-7461 – Boundary error when parsing option 119 data in DHCP packets in dhclient(8). Attacker on the network can send crafted data to DHCP client

CVE-2016-20009 – Stack-based overflow on the message decompression function.

CVE-2020-15795 – DNS domain name label parsing functionality does not properly validate the names in DNS responses. Parsing malformed responses could result in a write past the end of an allocated structure.

CVE-2020-27009 – DNS domain name record decompression functionality does not properly validate the pointer offset values. Parsing malformed responses could result in a write past the end of an allocated structure.

CVE-2020-27736 – DNS domain name label parsing functionality does not properly validate the name in DNS responses. Parsing malformed responses could result in a write past the end of an allocated structure.

CVE-2020-27737 – DNS response parsing functionality does not properly validate various length and counts of the records. Parsing malformed responses could result in a read past the end of an allocated structure

CVE-2020-27738 – DNS domain name record decompression functionality does not properly validate the pointer offset values. Parsing malformed responses could result in a read access past the end of an allocated structure

CVE-2021-25677 – DNS client does not properly randomize DNS transaction ID (TXID) and UDP port Numbers

Unnamed NetX exploit – two functions in the DNS resolver fo not check that the compression pointer does not equal the same offset currently being parsed, potentially leading to an infinite loop

Protection

Against nearly all exploits, the first step is to patch all systems. Following this, users should follow the mitigation steps outlined by Forescout.

When IoT devices are protected, it’s important that individuals, family’s, and business owners take the steps to protect their other device. These steps include using the right tools to ensure they’re protected – One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

W-2 Phishing Scam Targets 2021 Tax Season

Phishing scams are always prevalent, but tax season tends to step things up a few gears. Threat actors are carrying out a new attack campaign, using phishing emails and a TypeForm exploit to try to steal victims’ login credentials. TypeForm is a website that allows users to conduct surveys and create quizzes; it has a legitimate use. Hackers are using exploits within TypeForms framework to create fraudulent login pages as a part of the phishing scam.

A new report by Armorblox details the attack, in which the phishing scam takes advantage of the 2021 tax season by pretending to be a W-2 tax document shared via Microsoft OneDrive.

The phishing scam starts with victims receiving an email purporting to be from OneDrive, where a file named ‘2020_TaxReturn&W2.pdf’ is shared with the user.

W-2 Phishing Email

Previously, companies sent tax-related correspondence via mail, but in recent times many have switched to email for various documents, such as 1099 and W-2.

It is important to note that the above email does not stand up to any kind of examination by someone trained or educated to keep an eye out for phishing emails. Regardless, this phishing scam has been successful.

If the victim clicks on the link, they are brought to a TypeForm form that includes a blurred out 2020 W-2 tax document pretending to be secured by the Adobe Secure Document service.

The form will request that the visitor enter their email address and password to log in and retrieve the W-2 document.

When entering details, the document will consistently state the details are incorrect, before eventually displaying a message which reads, “Unable to verify your identity”.

ArmorBlox noted this is the heart of the scam; the hackers are using trying to make the user enter all of their password and username combinations they can think of, while harvesting them unbeknownst to the victim.

“It’s likely that the error messages could be a smokescreen for the attackers to gather as many account ID and password combinations as unsuspecting victims are willing to enter in an attempt to brute-force their way to gain access to the W2. In reality, there is no W2 pot of gold at the end of this malicious rainbow,” ArmorBlox explains in their report.

In their own research of this scam, BleepingComputer noted, “TypeForm is not the only legitimate form creation service to be abused by threat actors. Other phishing campaigns have used Google Forms and Canva to steal login credentials. Microsoft Forms is also heavily abused, which has led Microsoft to proactively warn IT admins when they detect phishing campaigns abusing Microsoft Forms in their Active Directory tenants.”

Rise in Phishing Scams During the 2021 Tax Season

More than any other, the 2021 tax season has been rife with cybercrime and scams. The delayed start and COVID pandemic have led to fertile soils for hackers trying to make a quick buck from phishing campaigns on unware users.

“It’s like the perfect storm we’re dealing with right now,” said Howard Silverstone, a forensic accountant and a member of the American Institute of Certified Public Accountants’ fraud task force.

Much of the fraud typically involves identity theft, according to tax experts. In such cases, a criminal might steal personal information to file a fake tax return and collect your refund.

Taxpayers may also unwittingly supply personal data to criminals who falsely claim they can help collect stimulus checks, according to the IRS. Congress is aiming to pass a $1.9 trillion Covid relief bill that includes $1,400 stimulus checks by mid-March.

“Thousands of people have lost millions of dollars and their personal information to tax scams,” according to the IRS.

More than 89,000 Americans filed a complaint with the Federal Trade Commission last year reporting tax fraud linked to identity theft, according to the consumer agency. Identity theft was the most reported type of fraud in 2020, the FTC said.

Criminals often reach out via telephone and e-mail to try ripping off unsuspecting victims.

In IRS imposter scams, for example, a con artist may pose as an IRS agent and try to intimidate callers into divulging sensitive information. Phishing scams aim to get data like account information and passwords through bogus websites, texts and emails.

However, the IRS won’t initiate contact taxpayers by email, text message or social media channels to request personal or financial information. The agency also won’t call to demand immediate payment — officials will generally first mail a bill to any taxpayer who owes taxes.

Protection against Phishing Attacks

The key in defending against phishing is always education. Business leaders should ensure employees receive regular cybersecurity training to be able to spot fraudulent emails. There are always occasions when phishing scams are so high-fidelity that they can rarely be spotted by the naked eye, and in this case a number of cybersecurity tools should be available to discern the legitimacy of possible scams. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

North Korean-backed Lazarus Group Attack Freighters With New Vyveva Malware

North Korean-back Lazarus Group has been using a new malware with backdoor capabilities in an ongoing campaign against South African freighters and logistics companies. The malware, dubbed Vyveva, was first reported on by researchers at ESAT last year. While Vyveva was only found on a handful of freighters by ESAT, it is understood that the malware has infected several ships that have yet to be reported.

The Vyveva malware comes with an extensive toolkit, allowing Lazarus Group operators to harvest and exfiltrate files from infected systems to servers under their control using the Tor anonymous network as a secure communication channel.

Lazarus Group can also use the malware to delivery and execute malicious code on any compromised system on the target network, making propagation a big threat in the campaign.

According to BleepingComputer, Vyveva boasts many other features, including support for timestomping commands, which allows its operators to manipulate any file’s date using metadata from other files on the system or by setting a random date between 2000 and 2004 to hide new or modified files.

“While the backdoor will connect to its command-and-control (C2) server once every three minutes, it also uses watchdogs designed to keep track of newly connected drives or the active user sessions to trigger new C2 connections on a new session or drive events.” BleepingComputer reported.

ESAT noted several similarities between Vyveva and other malware strains developed by Lazarus Group. The use of a fake TLS protocol in network communication, command-line execution chains, and the methods of using encryption and Tor services are all evidence of a Lazarus Group attack.

On the geographic scale of the attack, security researcher Filip Jurčacko said, “Vyveva constitutes yet another addition to Lazarus Group’s extensive malware arsenal. Attacking a company in South Africa also illustrates the broad geographical targeting of this APT group.”

Vyveva Malware Analysis

Much of this analysis was carried out by ESAT, and reported through welivesecurity.

As mentioned, there are a number of similarities between Vyveva and other Lazarus Group Malware strains. This is most notable when compared with the NukeSped remote-access-trojan.

Comparison of Vyveva and NukeSped, courtesy of welivesecurity

ESAT have found three of the multiple components comprising Vyveva – its installer, loader and backdoor. The installer is the earliest chronological stage found and since it expects other components to be already present on the machine, it suggests the existence of an earlier, unknown stage – a dropper. The loader serves to decrypt the backdoor using a simple XOR decryption algorithm.

Vyveva Components

The installer creates a service that ensures the persistence of the backdoor, as well as storing the backdoor configuration in the registry. The malware aims to create legitimate-looking services by taking combinations of words from existing services randomly selected.

The installer will first set the configuration infection ID, which is unique for each victim. This is also stored in the registry, along with a configuration for the encrypted C&C servers.

The backdoor is Vyveva’s main component. It connects to the C&C and executes commands from Lazarus Group, featuring 23 different commands. Most of them are ordinary commands for file and process operations or information gathering, but there is also a less common command for file timestomping.

The configuration of the backdoor, which is initially set by the installer, is read from the registry value. When the configuration is modified by a C&C command, the value stored in the registry is updated.

Config File from welivesecurity

Lazarus Group; Veteran Threat Actors

Lazarus Group first came into the public spotlight when they carried out Operation Troy, which ran between 2009 and 2012.

Operation Troy was a series of distributed denial-of-service (DDos) attacks targeting government establishments in Seoul, South Korea.

Lazarus Group made the news again, identifying themselves as ‘Guardians of Peace’, in November 2014 for carrying out the Sony Pictures hack. During the attack, confidential data of many Sony Pictures employees were released, and initially circulated on Reddit. This attack is notable in the history of Lazarus Group; it was carried out in a sophisticated and complex manner, showing the group were now developing their skills rapidly.

Lazarus Group have also been responsible for a number of digital bank-heists; and the amount seized is believed to be at least $97 million.

The WannaCry ransomware attack of 2017, which saw a number of healthcare systems including the NHS in the UK brought to a halt, is believed but not confirmed to have been carried out by Lazarus Group.

Recently, Lazarus Group are involved in a number of additional attacks, notable the late-2020 pharmaceutical company attacks. By using spear-phishing methods, members of Lazarus Group acted as health officials and reached out to a number of pharmaceutical companies. Once trust was gained, Lazarus Group sent a number of malicious links to the companies. It is unconfirmed what the goal of the attack was, but it is suspected that they were looking to sell data for profit, extort the companies and their employees, and give foreign entities access to proprietary COVID-19 Research.

Protection

Organizations like Lazarus Group show that there are few industries that malware cannot affect. Business owners should be vigilant in their cybersecurity suite and use proactive tools in the fight against malware. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

REvil Ransomware New Update Allows it to Encrypt in Safe Mode

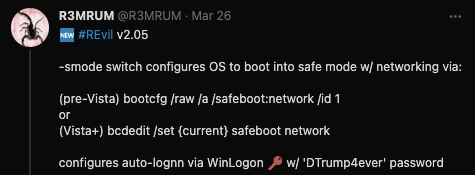
Evil Ransomware, already a major threat in the world of cybersecurity, has gotten a new update to give it extra fangs. In March, the Ransomware was developed further to give it the ability to encrypt in safe mode. This mode can be enabled using the -smode command-line argument, which would reboot the device into Safe Mode, where it would perform the encryption of files. However, the ransomware required someone to manually login to Windows Safe mode before the encryption would start, which could raise red flags. This week, another update came for REvil. This time, the ransomware was able to change the login credentials and cause an automatic re-log after restarting, fully automating the infection process.

It is believed that these features were added to REvil Ransomware in order to evade detection by the hosts cybersecurity software. Furthermore, it would shut down backup software, database servers, or mail servers to have greater success when encrypting files.

The updates were reported on and analysed by security researcher R3MRUM.

REvil, upon infection, will edit several settings within the Windows Registry. Specifically, it sets the auto-login to “1”, the default user name to the account name, and the password to “DTrump4ever”.

REVIL screenshot
R3MRUM’s analysis on the registry changes

It is unknown if all samples of REvil Ransomware will use this password, however at least two uploaded to VirusTotal have it enabled.

REvil has been at the forefront of ransomware attacks for a long time, and this update will ensure it remains there. The gang grew more aggressive in recent attacks; when victims refused to pay, they called journalists to report the companies breach. There have also been several reports since the start of 2021 of the gang threatening victims with DDOS attacks if they don’t pay up.

REvil Ransomware: A Storied History

Acer Images 2

REvil is a Ransomware-as-a-Service (RaaS), meaning it can be sold on a subscription basis and is usable by just about anybody. In the last 12 months, it has extorted large amounts of money for corporations and individuals. According to researchers, it is the most widespread ransomware strain. Groups using have a knack for shaking down businesses that don’t meet their demands, often through threats or leaking dating.

REvil, also known as Sodinokibi, first appeared in April 2019 and rose to prominence after another RaaS gang called GandCrab shut down its service. In the early days of REvil, researchers and security firms identified it as a strain of GandCrab, or at least established multiple links between the two. An alleged member of the group, using the handle Unknown, confirmed in an interview that the ransomware was not a new creation and that it was built on top of an older codebase that the group acquired.

The group behind REvil Ransomware and other groups selling RaaS often do so on a commission basis. Usually, this means a cut of between 20% and 30% of the money earned through infecting victims with ransomware.

In 2020, the IBM Security X-Force Incident Response reported that 1 in 3 Ransomware infections were caused by REvil.

In February, the REvil ransomware operation posted a job notice where they were looking to recruit people to perform DDoS attacks and use VOIP calls to contact victims and their partners.

In March, a security researcher known as 3xp0rt discovered that REvil has announced that they were introducing new tactics that affiliates can use to exert even more pressure on victims.

These new tactics include a free service where the threat actors, or affiliated partners, will perform voice-scrambled VOIP calls to the media and victim’s business partners with information about the attack. The ransomware gang is likely assuming that warning businesses that their data may have been exposed in an attack on of their partners, will create further pressure for the victim to pay.

REvil is also providing a paid service that allows affiliates to perform Layer 3 and Layer 7 DDoS attacks against a company for maximum pressure. A Layer 3 attack is commonly used to take down the company’s Internet connection. In contrast, threat actors would use a Layer 7 attack to take down a publicly accessible application, such as a web server.

Protection

For threats like REvil, it is important to have a proactive approach, rather than reactive. Reactive cybersecurity is effectively useless against threats like this, when a device can be rebooted in safe mode immediately. It is critical that business leaders use proactive tools like SaferNet to ensure their businesses are protected.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.