Iranian Airline Struck By Cyberattack

Mahan Air, one of Iran’s largest airlines, has been hit by a cyberattack. The cyberattack caused operations to go offline and lead to a possible data breach or data loss.

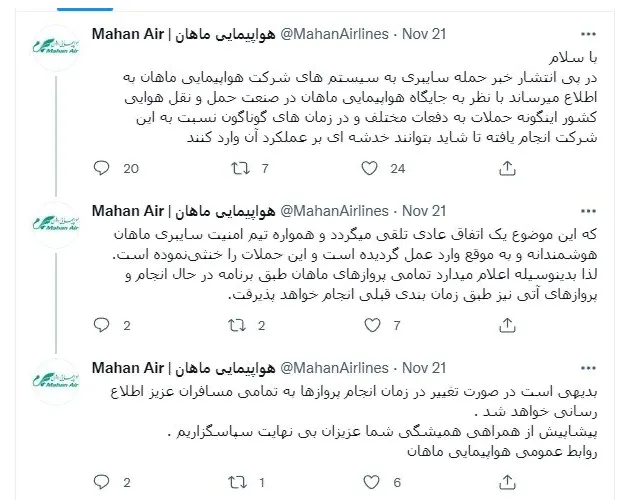
The firm announced the cyberattack on Twitter, though dealing with hackers is not uncommon for Mahan Airs’ IT security teams.

Customers are unable to access the airline’s website to book flights, but all international and domestic flights are running as usual without delays.

Moreover, the company claims that the attack has been thwarted successfully and in a short time, downplaying its significance and disregarding any real impact.

“Following the news of the cyberattack on the systems of Mahan Airlines, it is reported that due to the position of Mahan Airlines in the country’s aviation industry, such attacks have been carried out against this company many times and at different times, so that they may be damaged,” reads the translated tweet by Mahan airlines.
Screenshot 2021 11 23 at 14.35.52

“This is considered a normal occurrence and Mahan Cyber Security Team has always acted intelligently and in a timely manner and has thwarted these attacks. Therefore, it hereby announces that all Mahan flights will be operated according to the schedule and future flights will be operated according to the previous schedule.”

Mahan Air was added to the US sanctions list in 2011 for supporting members of Iran’s Islamic Revolutionary Guard Corps (IRGC).

In 2019, the US Treasury published a statement on Mahan Air’s operation, detailing the following:

“Mahan Air has transported IRGC-QF operatives, weapons, equipment, and funds abroad in support of the IRGC-QF’s regional operations, and has also moved weapons and personnel for Hizballah.”

“Since the onset of the Syrian civil war, Mahan Air has routinely flown fighters and materiel to Syria to prop up the Assad regime, which has contributed to mass atrocities and displacement of civilians.”

Although Mahan’s operations oppose American strategic interests, which led to actual military action in July 2020, the hackers responsible for the most recent incident don’t seem to be Americans.

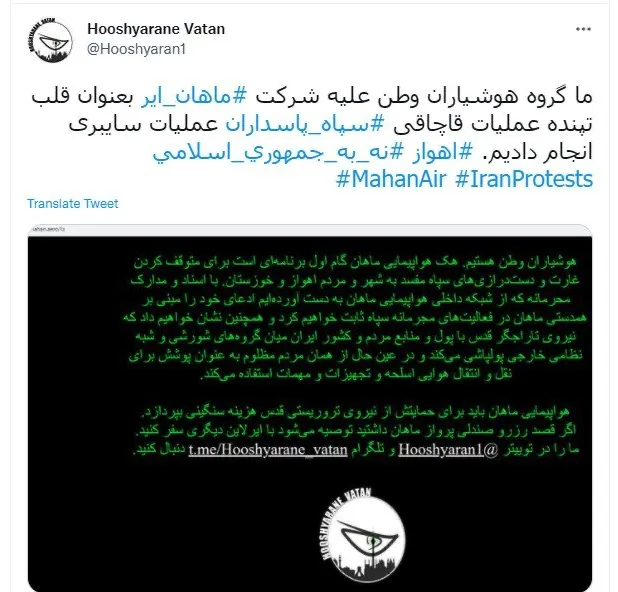
The hacker who took responsibility for the cyberattack is ‘Hooshyarane Vatan,’ who sees IRGC as their enemy and says they fight for the rights of the Ahwaz minority (Iranian Arab minority).

Vatan claims to have stolen confidential documents that expose how the airline has worked with the IRGC and threatened to publish names, numbers, and proof of Mahan’s activities.

“Hacking Mahan Airlines is the first step of a program to stop the looting and encroachments of the corrupt corps on the city and the people of Ahvaz and Khuzestan. With the confidential documents we have obtained from the internal network of Mahan Airlines, we will prove our claim of Mahan complicity in the criminal activities of the IRGC, and we will also show that the Quds force is looting the money and resources of the people and the country of Iran among insurgent groups,” reads a translated text from the alleged hackers.

“And the foreign militia squanders money and at the same time uses the same oppressed people as cover for the air transport of weapons, equipment and ammunition.”
Screenshot 2021 11 23 at 14.36.29

As the actors wrote on their Telegram channel, they have proof of the airline hiding military shipments in civilian flights to secure them from attacks.

This reporting culminated with the indictment of two Iranian cyber-actors who attempted to influence American voters between September and November 2020, promoting false information under the ‘Proud Boys’ attire.

Both of the identified actors allegedly worked for a cybersecurity company that provided services to the Iranian government.

Protection Against Cyberattacks

There are several tools internet users should use to increase their online protection. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.
TSA Phishing and Scam Sites Take Aim At US Travelers

There has been a swift uptick in reports of phishing and scams related to TSA PreCheck, Global Entry, and NEXUS application service sites, in which customers are being charged $140 to receive nothing in return.

Initial reports appeared in March 2021, and by July threat actors were abusing Google Ads to promote fake TSA websites on Google to increase traffic.

A recent report by Abormal Security confirms that the scam sites and phishing activities are still ongoing, and indeed increasing as the Christmas travel season approaches.

TSA PreCheck is a program that allows people to pass through a quicker and easier screening process at the airport.

People who enroll in the program receive a background check once and can then travel across the US without removing personal items or going through vigorous checks each time they fly.

Especially during the pandemic, when people seek to spend the minimum amount of time in crowded places, there’s an increasing number of travelers who sign up for this program.

The TSA PreCheck needs to be renewed every five years, which costs members $70 (down from $85).

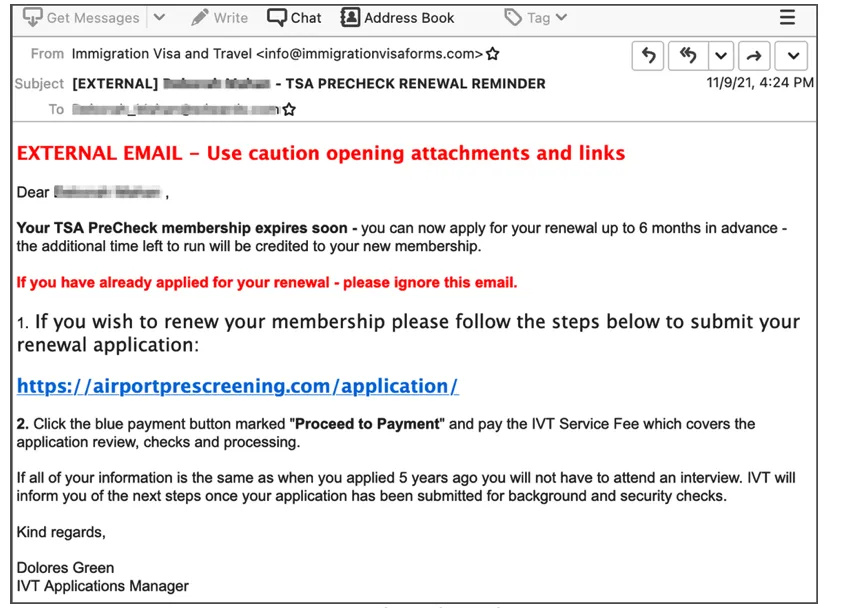
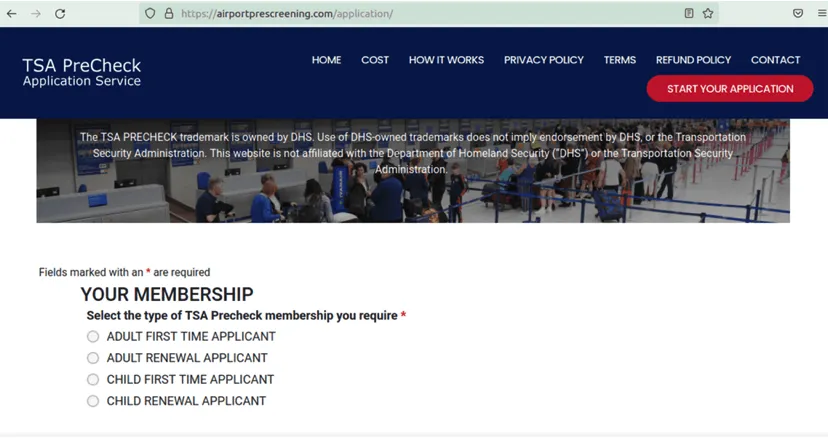
Threat actors are sending phishing emails to individuals informing them of the expiration of their TSA PreCheck membership, and attempting to convince to renew by following an embedded URL.

Screenshot 2021 11 23 at 13

These emails take the victim to fake renewal sites that were made to appear legitimate and also use convincing domain names such as:

  • airportprescreen[.]com
  • airportprescreening[.]com
  • applyfornexuscard[.]com
  • assist-gov[.]com
  • applyglobaltraveler[.]com
  • easynexusapplication[.]com
  • fastpassapplication[.]com
  • lowrisktraveler[.]com
  • immigrationvisaforms[.]com
  • travelauthorizationusa[.]com

Using a top-level domain such as ‘.com’ adds a sense of legitimacy to unsuspecting targets, increasing the chance of scamming a target.

Screenshot 2021 11 23 at 13.5

Many of the phishing/scam sites seen by Abnormal Security include an interesting disclaimer, which states buyers don’t have a guaranteed chance of success with the renewal.

“We are not the United States government or associated with it. There are no guarantees you will be granted a known traveler number by the government. We try to make sure everything is submitted correctly to eliminate rejections from submission errors.”

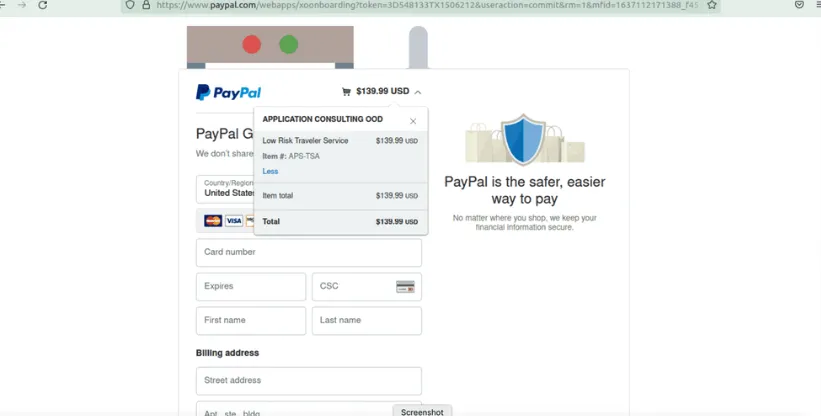
This may be missed easily, given that people generally don’t read service disclaimers. However, the fact that Paypal is the only available payment method should tip individuals off that the phishing site is not legitimate.

The regular fee is $70, while the threat actors list their price at $139.99

Screenshot 2021 11 23 at 13.58.30

Abnormal Security recommends that if an individual wishes to renew TSA PreCheck, Clear, or Global Entry membership that they should not Google, as it is likely they will encounter a bogus ad.

Instead, visit the Homeland Security’s Trusted Traveler Programs page, which contains the legitimate URLs for all available travel programs.

Protection Against Phishing

Attacks like the Conti Ransomware campaign show that cyberattacks are increasing at an exponential rate, and both government and business leaders are underprepared to face the fallout of an attack. There are several tools internet users should use to increase their online protection. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.
Accenture Discloses Data Breach After LockBit Ransomware Attack

IT consultancy giant Accenture has confirmed that the LockBit Ransomware gang made off with data during an attack that hit its systems in August. The details of the heist were revealed in the company’s financial report for the fourth quarter and full fiscal year, which ended on August 31, 2021.

“In the past, we have experienced, and in the future, we may again experience, data security incidents resulting from unauthorized access to our and our service providers’ systems and unauthorized acquisition of our data and our clients’ data including inadvertent disclosure, misconfiguration of systems, phishing ransomware or malware attacks,” Accenture said.

“During the fourth quarter of fiscal 2021, we identified irregular activity in one of our environments, which included the extraction of proprietary information by a third party, some of which was made available to the public by the third party.

“In addition, our clients have experienced, and may in the future experience, breaches of systems and cloud-based services enabled by or provided by us.”

The LockBit Ransomware gang claimed that they stole 6TB of data from Accenture, after which they demanded a $50 million ransom.

Although Accenture has mentioned the attack within SEC filings and filed data breach notification letters, the company has yet to make a public statement of the LockBit Ransomware attack or acknowledge it in any other manner.

This likely means that the stolen data didn’t contain any personally identifiable information (PII) or protected health information (PHI) data which would’ve triggered regulatory notification requirements.

At the time of the LockBit Ransomware attack, Accenture managed to restore all affected systems from backups, with little impact on business operations.

In September, the company claims made by the LockBit Ransomware gang that network credentials belonging to customers were stolen.

In September, the company denied claims made by the LockBit gang that they also stole credentials belonging to Accenture customers that would enable them to compromise their networks.

“We have completed a thorough forensic review of documents on the attacked Accenture systems. This [LockBit’s] claim is false,” Accenture told researchers at BleepingComputer, denying that customer credentials were stolen in the August ransomware attack.

“As we have stated, there was no impact on Accenture’s operations, or on our client’s systems. As soon as we detected the presence of this threat actor, we isolated the affected servers.”

Accenture is a Fortune 500 company and one of the world’s largest IT services and consulting firms with more than 624,000 employees across 120 countries, providing services to a wide array of industry sectors, including banks, government, technology, energy, telecoms, and more.

LockBit Ransomware Analysis

NOTE: This analysis of Lockbit Ransomware was carried out by McAfee

The file found in the investigation of Lockbit Ransomware was a dropper renamed as a .png file. When first opening the .png files we were expecting a real image file, with perhaps some steganography inside, but what we saw instead was the header of a portable executable, so no steganography pictures this time. The PE was compiled in Microsoft Visual C# v7.0 / Basic .NET, .NET executable -> Microsoft.

Entropy-wise is tidy too, not showing any stray sections or big spikes in the graph. This behavior indicates that the writer of the Lockbit Ransomware did not use obfuscation.

This file is a .NET launcher. Examining the Main() function in the code shows that an array containing a particularly long AES encrypted base64 string (in the variable named ‘exeBuffer’) carries the executable for the actual ransomware.

This encrypted string is decrypted using the key ENCRYPTION29942. The first 32 bytes of the long ExeBuffer string are used as the salt in the encryption scheme, where ENCRYPTION29942 is the passphrase.

The script checks for the existence of vbc.exe on its designated host. Usually, this binary is a digitally signed executable from Microsoft; however, in this case, the malware uses it for process hollowing.

By statically analyzing the file we can spot the usage of:

  • NtUnmapViewOfSection
  • LockBit Ransomware uses this API in order to unmap the original code in execution
  • NtWriteVirtualMemory
  • The malware writes the base address of the injected image into the PEB via NtWriteVirtualMemory
  • VirtualAllocEx
  • To allocate the space before injecting the malicious code
  • The VBC utility is the visual basic compiler for Windows and LockBit Ransomware uses it to compile and execute the code on the fly directly in execution. If the vbc utility does not exist on the system, the malware downloads the original vbc.exe file from the same malicious URL as seen before. After executing vbc.exe, the malware replaces the objects in memory with the code for deploying the ransomware (as deduced from the exeBuffer).

The list of services LockBit Ransomware tries to stop are:

  • DefWatch (Symantec Antivirus)
  • ccEvtMgr (Norton AntiVirus Event Manager)
  • ccSetMgr (Common Client Settings Manager Service of Symantec)
  • SavRoam (Symantec Antivirus)
  • sqlserv
  • sqlagent
  • sqladhlp
  • Culserver
  • RTVscan (Symantec Antivirus Program)
  • sqlbrowser
  • SQLADHLP
  • QBIDPService (QuickBooksby Intuit.)
  • QuickBoooks.FCS (QuickBooksby Intuit.)
  • QBCFMonitorService (QuickBooksby Intuit.)
  • sqlwriter
  • msmdsrv (Microsoft SQL Server Analysis or Microsoft SQL Server)
  • tomcat6 (Apache Tomcat)
  • zhundongfangyu (this belongs to the 360 security product from Qihoo company)
  • vmware-usbarbitator64
  • vmware-converter
  • dbsrv12 (Creates, modifies, and deletes SQL Anywhere services.)
  • dbeng8 (Sybase’s Adaptive Server Anywhere version 8 database program)
  • wrapper (Java Service?)


If one of these services is found by the malware querying the status of it, with the function “QueryServiceStatusEx”, LockBit will get all the depending modules when correct and safe and it will stop the service with the function “ControlService”.

The ransom note is rather compact because the author hardcoded the content right in the code without using any obfuscation or encryption. The text file containing the ransom note is created in every directory after encryption and called Restore-My-Files.txt.

Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Sinclair Broadcast Taken Down By Ransomware

TV Stations owned by the Sinclair Broadcast Group were taken down across the US due to a ransomware attack last weekend.

Sinclair Broadcast Group is a Fortune 500 media company (with annual revenues of $5.9 billion in 2020) and a leading local sports and news provider that owns multiple national networks.

Its operations include 185 television stations affiliated with Fox, ABC, CBS, NBC, and The CW (including 21 regional sports network brands), with approximately 620 channels in 87 markets across the US (amounting to almost 40% of all US households).

This is the second incident that impacted Sinclair’s TV stations in July 2021, when the company asked all Sinclair stations to change passwords “as quickly as possible” following a security breach.

It is believed the ransomware attack shut down Active Directory services for the domain, leading to wide disruption throughout the entire organization and affiliates by blocking access to domain resources across the network

Several corporate assets were taken down in the incident, including the email servers, broadcasting, and newsroom systems, forcing TV stations to create Gmail accounts to receive news tips from viewers and use PowerPoint for newscasts graphics.

The company released a statement saying, “On October 16, 2021, the Company identified and began to investigate and take steps to contain a potential security incident. On October 17, 2021, the Company identified that certain servers and workstations in its environment were encrypted with ransomware, and that certain office and operational networks were disrupted. Data also was taken from the Company’s network. The Company is working to determine what information the data contained and will take other actions as appropriate based on its review.

Promptly upon detection of the security event, senior management was notified, and the Company implemented its incident response plan, took measures to contain the incident, and launched an investigation. Legal counsel, a cybersecurity forensic firm, and other incident response professionals were engaged. The Company also notified law enforcement and other governmental agencies. The forensic investigation remains ongoing.

While the Company is focused on actively managing this security event, the event has caused – and may continue to cause – disruption to parts of the Company’s business, including certain aspects of its provision of local advertisements by its local broadcast stations on behalf of its customers. The Company is working diligently to restore operations quickly and securely.

As the Company is in the early stages of its investigation and assessment of the security event, the Company cannot determine at this time whether or not such event will have a material impact on its business, operations or financial results.”

While regional sports channels were largely not affected by the incident, there are reports that, in some US markets, local NFL games were replaced by national sports programming (such as bowling).

A sinclair spokesperson said of the ransomware attack, “Sinclair Broadcast Group recently identified a cybersecurity incident involving our network. As a result of the incident, certain devices were encrypted with ransomware, data was taken from our environment, and certain business operations have been disrupted. Senior management was notified, and we implemented our incident response and business continuity protocols, took measures to contain the incident, and launched an investigation. A cybersecurity firm that has assisted other companies in similar circumstances was engaged, and law enforcement and other governmental agencies were notified.

We are working diligently to address the incident and to restore operations quickly and securely. As we work to complete the investigation, we will look for opportunities to enhance our existing security measures. We appreciate your patience and understanding as we work through this incident.”

Protection Against Ransomware

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Evil Corp Release New Macaw Locker Ransomware To Evade US Sanctions Again

Evil Corp has launched a new strain called Macaw Locker Ransomware to evade US sanctions which in the past has prevented victims from making ransom payments. Evil Corp, which has gone under a number of monikers such as Indrik Spider and the Dridex gang, is a veteran of the cybercrime world. It has been active since 2007, usually as an affiliate to other cybercrime outfits.

As time passed, Evil Corp began to shift to their own attacks by creating their own malware. At their peak, their signature strain was a banking trojan known as Dridex us in phishing attacks.

As ransomware attacks took over the cybercrime scene as the most profitable hacking vehicle, Evil Corp launched BitPaymer, delivered via the Dridex malware to compromised corporate networks.

The gang’s success and notoriety lead to them being sanctioned by the US government in 2019.

Due to these sanctions, ransomware negotiation firms will no longer facilitate ransom payments for operations attributed to Evil Corp.

To bypass the restrictions, Evil Corp created a plethora of limited-use ransomware strains and operations under names like WastedLocker, Hades, Phenoix Locker, and PayloadBin.


Macaw Loader Ransomware Analysis

Last week, SaferNet reported that Olympus and Sinclair broadcasting group has their operations disrupted by a ransomware attack.

For Sinclair, this mean several broadcasts needed to be canceled, old shows were rerun, and newscasters had to report their stories with whiteboards and paper.

It was unknown what strain caused these attacks at the time, with most sources pointing to Black Matter Ransomware. However, it is now understood that the strain was Evil Corp’s new strain, Macaw Locker Ransomware

Emsisoft CTO Fabian Wosan explained in a conversation with researchers at Bleeping Computer that he made the discovery based on a code analysis of Macaw Locker Ransomware versus other strains in Evil Corp’s ransomware family.

It is currently believed that Sinclair and Olympus are the only victims of Macaw Locker Ransomware thus far.

Sources also shared the private Macaw Locker Ransomware victim pages for two attacks, where the threat actors demand a 450 bitcoin ransom, or $28 million, for one attack and $40 million for the other victim.

It is unknown what company is associated with each ransom demand.

The Macaw Locker ransomware will encrypt victims’ files and append the .macaw extension to the file name when conducting attacks.

While encrypting files, the ransomware will also create ransom notes in each folder named macaw_recover.txt. For each attack, the ransom note contains a unique victim negotiation page on the Macaw Locker Ransomware’s Tor site and an associated decryption ID, or campaign ID, as shown below.

The gang’s dark web negotiation site contains a brief introduction to what happened to the victim, a tool to decrypt three files for free, and a chatbox to negotiate with the attackers.

Now that Macaw Locker Ransomware has been exposed as an Evil Corp variant, we will likely see the threat actors rebrand their ransomware again.

As stated by researchers at Bleeping computer, “This constant cat-and-mouse game will likely never end until Evil Corp stops performing ransomware attacks or sanctions are lifted.”

Both of these events are unlikely.


Protection

Ransomware is a crowded scene, with new threats rising and falling almost every day. It is important that business owners and families have the best tools for the job when it comes to protecting their devices. One of these tools is SaferNet.

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Millions of Smartphone Users Scammed In UltimaSMS Scam

Hackers are using malicious Android apps, dubbed UltimaSMS, to trick users into signing up for a fraudulent SMS subscription service. The service eventually charges them hefty sums on their phone bills.

Jakub Vavra from Avast, who was one of the first to research the campaign, dubbed the apps UltimaSMS because the first app he discovered using this tactic was called Ultima Keyboard Pro.

“The fake apps I found feature a wide range of categories such as custom keyboards, QR code scanners, video and photo editors, spam call blockers, camera filters, and games, among others,” Vavra wrote in a blog post Monday.

The UltimaSMS campaign, which started in May, is compromised of roughly 151 apps that have at one point in their lifetime been on the Google Play Store. Collectively, the apps have been downloaded 10.5 million times.

Google has removed flagged apps from the store, but it is likely there are many more hidden within, Vavra noted. Google has had a storied history with malicious apps making their way onto the Play Store for months at a time.

All of the UltimaSMS offerings are “essentially copies of the same fake app used to spread the premium SMS scam campaign,” Vavra explained, which he said likely indicates that one bad actor or group is behind the entire campaign.

Vavra observed that the apps advertised seem legitimate, but upon closer inspection, there is something more suspicious. For instance, they tend to include generic privacy policy statements and feature basic developer profiles including generic email addresses, as well as numerous negative reviews that identify them as fraudulent.

Citing insights from mobile marketing intelligence firm Sensor Tower, he said the campaign appears to be global, ensnaring users from more than 80 countries.

“The apps have been most downloaded by users in the Middle East, such as Egypt, Saudi Arabia, Pakistan, followed by users in the U.S. and Poland,” Vavra explained.

The hackers behind UltimaSMS are spreading their campaign with “numerous catchy video advertisements” posted on advertising channels of social-media sites like Facebook, Instagram and TikTok, Vavra explained.

If an Android user falls for the trick and installs one of the apps, it checks their location, International Mobile Equipment Identity (IMEI), and phone number to determine which country area code and language to use for the scam, according to the post.

“Once the user opens the app, a screen, localized in the language their device is set to, prompts them to enter their phone number, and in some cases email address, to gain access to the app’s advertised purpose,” Vavra wrote.

Once the user enters the details, the app subscribes him or her to a premium SMS service that sends texts to a short-coded number — each text results in a charge for the user. These charges can total upwards of $40 per month depending on the country and mobile carrier.

And, instead of unlocking the apps’ advertised features, the apps will either display further SMS subscriptions options or stop working altogether, he explained.

“The sole purpose of the fake apps is to deceive users into signing up for premium SMS subscriptions,” Vavra wrote.

Vavra points out that some of the apps actually describe their intention in the fine print, though many don’t, “meaning many people who submitted their phone numbers into the apps might not even realize the extra charges to their phone bill are connected to the apps,” he explained.

The apps collect premium SMS charges from subscribers typically to the maximum limit possible for their particular country, according to Vavra. Sometimes carriers will alert users of the excessive charges, but they also may go unnoticed for weeks or months, Vavra wrote.

Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

Hackers Inject Malware Via Google Chrome

An on-going phishing and spearphishing campaign is currently taking place, aiming to steal Office 365. The phishing emails appear as if they come from major brands, including Kaspersky.

According to a Kaspersky post from Monday, two phishing kits identified as “Iamtheboss” and “MIRCBOOT’ are being used together by multiple threat actors to send fake fax notifications.

“The phishing e-mails are usually arriving in the form of ‘fax notifications’ and lure users to fake websites collecting credentials for Microsoft online services,” according to the post.

One phishing campaign tracked by cybersecurity researchers abuses an Amazon service called Amazon Simple Email Service (SES). SES is designed to let developers deliver email from apps. The campaign relies on a stolen SES token used by a third-party contractor during the testing of the website 2050.earth.

The 2050.earth site is a Kaspersky project that features an interactive map illustrating what futurologists predict to be the future impact of technology on the planet. The stolen SES token is tied to Kaspersky and SES because the 2050.earth site is hosted on the Amazon infrastructure.

“These emails have various sender addresses, including but not limited to [email protected]. They are sent from multiple websites including Amazon Web Services infrastructure,” the security bulletin warned. The company said the stolen SES token was only abused in a limited capacity relative to an otherwise large-scale campaign abusing multiple brands.

It’s unclear what other brands, and how many, are impacted by the ongoing campaigns. It is believed that other non-Kaspersky SES tokens are involved

The company said the SES token was immediately revoked when it was identified as being stolen and abused.

The theft caused no damage, according to the advisory. “No server compromise, unauthorized database access or any other malicious activity was found at 2050.earth and associated services,” it said.

Office 365 credentials are a very common target for phishing attacks. In March, a phishing scam targeted executives in the insurance and financial sectors in an attempt to harvest Office 365 credentials to launch business email compromise (BEC) attacks.

Hackers abusing SES tokens are trying to give their emails a sense of legitimacy, by identifying themselves as coming from trusted companies.

Analysis showed that the phishing campaigns are relying on a phishing kit that Kaspersky researchers have named “Iamtheboss,” used in conjunction with another phishing kit known as “MIRCBOOT.”

The MIRCBOOT phishing kit was previously used in a large-scale phishing-as-a-service (PhaaS) campaign called BulletProofLink, which Microsoft previously discovered.

BulletProofLink provides phishing kits, email templates, hosting, and other tools that let users customize campaigns and develop their own phishing ploys. They then use the PhaaS platform to help with phishing kits, email templates, and the hosting services needed to launch attacks.

Protection Against Phishing

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

New Phishing Campaign Abuses Stolen Amazon SES Tokens

An on-going phishing and spearphishing campaign is currently taking place, aiming to steal Office 365. The phishing emails appear as if they come from major brands, including Kaspersky.

According to a Kaspersky post from Monday, two phishing kits identified as “Iamtheboss” and “MIRCBOOT’ are being used together by multiple threat actors to send fake fax notifications.

“The phishing e-mails are usually arriving in the form of ‘fax notifications’ and lure users to fake websites collecting credentials for Microsoft online services,” according to the post.

One phishing campaign tracked by cybersecurity researchers abuses an Amazon service called Amazon Simple Email Service (SES). SES is designed to let developers deliver email from apps. The campaign relies on a stolen SES token used by a third-party contractor during the testing of the website 2050.earth.

The 2050.earth site is a Kaspersky project that features an interactive map illustrating what futurologists predict to be the future impact of technology on the planet. The stolen SES token is tied to Kaspersky and SES because the 2050.earth site is hosted on the Amazon infrastructure.

“These emails have various sender addresses, including but not limited to [email protected]. They are sent from multiple websites including Amazon Web Services infrastructure,” the security bulletin warned. The company said the stolen SES token was only abused in a limited capacity relative to an otherwise large-scale campaign abusing multiple brands.

It’s unclear what other brands, and how many, are impacted by the ongoing campaigns. It is believed that other non-Kaspersky SES tokens are involved

The company said the SES token was immediately revoked when it was identified as being stolen and abused.

The theft caused no damage, according to the advisory. “No server compromise, unauthorized database access or any other malicious activity was found at 2050.earth and associated services,” it said.

Office 365 credentials are a very common target for phishing attacks. In March, a phishing scam targeted executives in the insurance and financial sectors in an attempt to harvest Office 365 credentials to launch business email compromise (BEC) attacks.

Hackers abusing SES tokens are trying to give their emails a sense of legitimacy, by identifying themselves as coming from trusted companies.

Analysis showed that the phishing campaigns are relying on a phishing kit that Kaspersky researchers have named “Iamtheboss,” used in conjunction with another phishing kit known as “MIRCBOOT.”

The MIRCBOOT phishing kit was previously used in a large-scale phishing-as-a-service (PhaaS) campaign called BulletProofLink, which Microsoft previously discovered.

BulletProofLink provides phishing kits, email templates, hosting, and other tools that let users customize campaigns and develop their own phishing ploys. They then use the PhaaS platform to help with phishing kits, email templates, and the hosting services needed to launch attacks.

Protection Against Phishing

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

SquirrelWaffle Malware Loader Causes Storm In Office365 Spam

SqurrelWaffle, a new malware loader, is firing out malware-loaded Microsoft Office documents to deliver Qakbot malware and the penetration-testing tool Cobalt Strike. Cisco Talos researchers said in a post last week they learned of the campaign in mid-September, when they spotted SquirrelWaffle in the initial stage of the infection chain.

The SquirrelWaffle campaign uses stolen email threads to appear as replies within those threads – A tactic identical to how Emotet malware spreads.

“The campaigns themselves feature several similar characteristics to the campaigns previously seen associated with established threats like Emotet,” Cisco Talos researchers explained.

“Due to the prevalence of these campaigns, organizations should be aware of SQUIRRELWAFFLE and the way it could be used by attackers to further compromise corporate networks,” they advised.

The SquirrelWaffle emails contain hyperlinks to malicious ZIP archives hosting the infected files on hacker-controlled web servers.

Most of the messages – 76 percent – are written in English. But the language used in the reply message shifts to match what was used in the original email thread, “demonstrating that there is some localization taking place dynamically,” Cisco Talos said. Besides English, the top five languages being used also include French, German, Dutch and Polish.

SquirrelWaffle isn’t quite as prolific as Emotet, at least not yet. However, the campaign has been growing steadily, as seen in the graph from Cisco Talos below.

“While the volume associated with these campaigns is not yet reaching the same level seen previously with threats like Emotet, it appears to be fairly consistent and may increase over time as the adversaries infect more users and increase the size of their botnet,” Cisco Talos predicted.

Researches noted that the malicious documents were crafted using some kind of automated builder. For example, in the recent campaigns, “the Microsoft Excel spreadsheets were crafted to make static analysis with tools like XLMDeobfuscator less effective,” they said.

The earliest files were submitted to public malware repositories on Sept. 10. Three days later, the campaign volume began to ramp up and “has been characterized by daily spam runs observed since then,” according to the writeup.

There are more signs that automation plays a part in the campaign.

“The URL structure of the SQUIRRELWAFFLE distribution servers appears somewhat tied to the daily campaigns, and rotates every few days,” according to the analysis.

Cisco Talos gave the example of the table, shown below, which depicts variance in the URL landing pages seen over a period of several days.


“This rotation is also reflected in the maldoc macros themselves, with the macro function names and hashes rotating at the same time,” the researchers added.

When a target falls for one of the emails and follows through on the link, they may download one of the loaded Office files – which have been split between Word and Excel files.

After opening whichever they receive, the SquirrelWaffle payload will be deployed.

In all of the SquirrelWaffle campaigns seen so far, the rigged links used to host the ZIP archives contain Latin words and follow a URL structure similar to this one:

abogados-en-medellin[.]com/odit-error/assumenda[.]zip

But in many cases, the campaign includes separate ZIP archives being hosted in different directories on the same domain. Inside of the ZIP archives, the malicious Office files often follow a naming convention similar to these examples:

  • chart-1187900052.xls
  • diagram-127.doc
  • diagram_1017101088.xls
  • Specification-1001661454.xls

It is believed the attack servers live on compromised WordPress sites.

The malware distribution campaigns are apparently jumping on previously compromised web servers: primarily those running versions of WordPress, with the most prevalent compromised version being WordPress 5.8.1.

Cisco Talos said that while the SquirrelWaffle threat is relatively new, the workings – including the distribution campaigns, infrastructure and command-and-control (C2) implementations – have a lot in common with those seen from other, more established threat actors.

“Organizations should continue to employ comprehensive defense-in-depth security controls to ensure that they can prevent, detect, or respond to SQUIRRELWAFFLE campaigns that may be encountered in their environments,” they recommended.

Protection Against SquirrelWaffle

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.

MediaMarkt Infected with $240 Million Hive Ransomware Attack

MediaMarket has become a victim of a Hive Ransomware attack with an initial ransom demand of $240 million. The attack has caused IT systems to shut down and physical store operations to be disrupted across Europe.

MediaMarkt has been operating since 1979 across 13 countries. The electronics manufacturer employs approximately 53,000 employees and has a total sales of €20.8 billion.

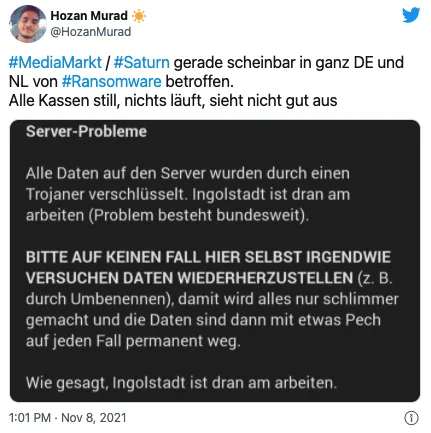
The company was hit by the Hive Ransomware attack on Sunday evening which rolled into Monday morning. The attack encrypted servers and workstations and led to the shutdown of IT systems to prevent the attack’s spread.

While online sales are still possible, cash registers cannot accept credit cards or print receipts at affected stores. The systems outage is also preventing returns due to the inability to look up previous purchases.

Screenshots posted on Twitter of alleged internal communications state that 3,100 servers were affected in this attack.

Reporters at BleepingComputer that the strain involved was Hive Ransomware, and that the demand was a stunning $240 million.

Ransomware gangs commonly demand large ransoms at the beginning to allow room for negotiation and usually receive a fraction of the initial demand. However, in the attack on MediaMarkt, it is believed the amount was almost immediately lowered.

While it is not clear if unencrypted data has been stolen as part of the attack, Hive ransomware is known to steal files and publish them on their ‘HiveLeaks’ data leak site if a ransom is not paid.

Reporters reached out to MediaMarkt today and received the following statement:

“The MediaMarktSaturn Retail Group and its national organizations became the target of a cyberattack. The company immediately informed the relevant authorities and is working at full speed to identify the affected systems and repair any damage caused as quickly as possible. In the stationary stores, there may currently be limited access to some services.

MediaMarktSaturn continues to be available to its customers via all sales channels and is working intensively to ensure that all services will be available again without restriction as soon as possible.

The company will provide information on further developments on the topic.”

Behind Hive Ransomware

Hive Ransomware is a newcomer to the Ransomware world, having launched in June 2021. However, it is has already gained a reputation for striking out at several healthcare providers and multinational companies.

The Hive Ransomware operators breach organizations using malware-ridden phishing campaigns.

Once the gang gains access to a network, they will spread laterally through a network while stealing unencrypted files to be used in extortion demands.

Once the threat actors eventually gain admin access on a Windows domain controller, they deploy Hive Ransomware throughout the network to encrypt all devices.

The Hive Ransomware gang are known to seek out and delete backups prior to encryption. This is to kneecap the victim and prevent them from using backups to escape the Ransomware attack.

Unlike other strains that operate on just Windows, Hive Ransomware comes in different flavors used to encrypt Linux and FreeBSD servers, commonly used to host virtual machines.

While many ransomware outfits follow a ‘code of honor’ type system in which they will not encrypt healthcare institutions, nursing homes, government agencies, and other essential services, Hive Ransomware is known to target anybody.

This has meant their reputation has spread like wildfire, just as their attacks do.

In August, this was shown when Hive ransomware attacked the non-profit Memorial Health System, which forced staff to work with paper charts and disrupted scheduled surgeries.

Protection

SaferNet is the perfect solution to the cybersecurity issues that individuals, families, and businesses face today. It not only connects every device using a secure, 24/7 always on, military grade VPN, but it also stops outside cyberthreats, malware and viruses as well. On SaferNet, all users are protected anywhere in the world, all the time, on any cellular or Wi-Fi network. In addition to SaferNet’s VPN and cyber protection, it also offers a range of employee or parental/family internet controls including internet filtering, monitoring, scheduling, and blocking access to websites or even entire website categories

Typically, a business or family would need 3 separate services for a VPN, Malware Protection, and Internet Controls; SaferNet offers all 3 features in one service. SaferNet truly is an endpoint security presence that can be implemented in minutes around the world, on phones, laptops, tablets, and computers at an economical price point that caters to all sizes of businesses and families. SaferNet guarantees a smooth setup and installation process that takes only minutes, and an easily accessible control hub for you to monitor all your employee’s or family members devices; including activity, time spent online, and threats blocked.